Watch at EaseStories. Answers. Perspective.

WATCH AT EASE · PRACTICAL GUIDE

Earlier coverage

Previously published coverage, with original dates preserved.

241–264 / 359

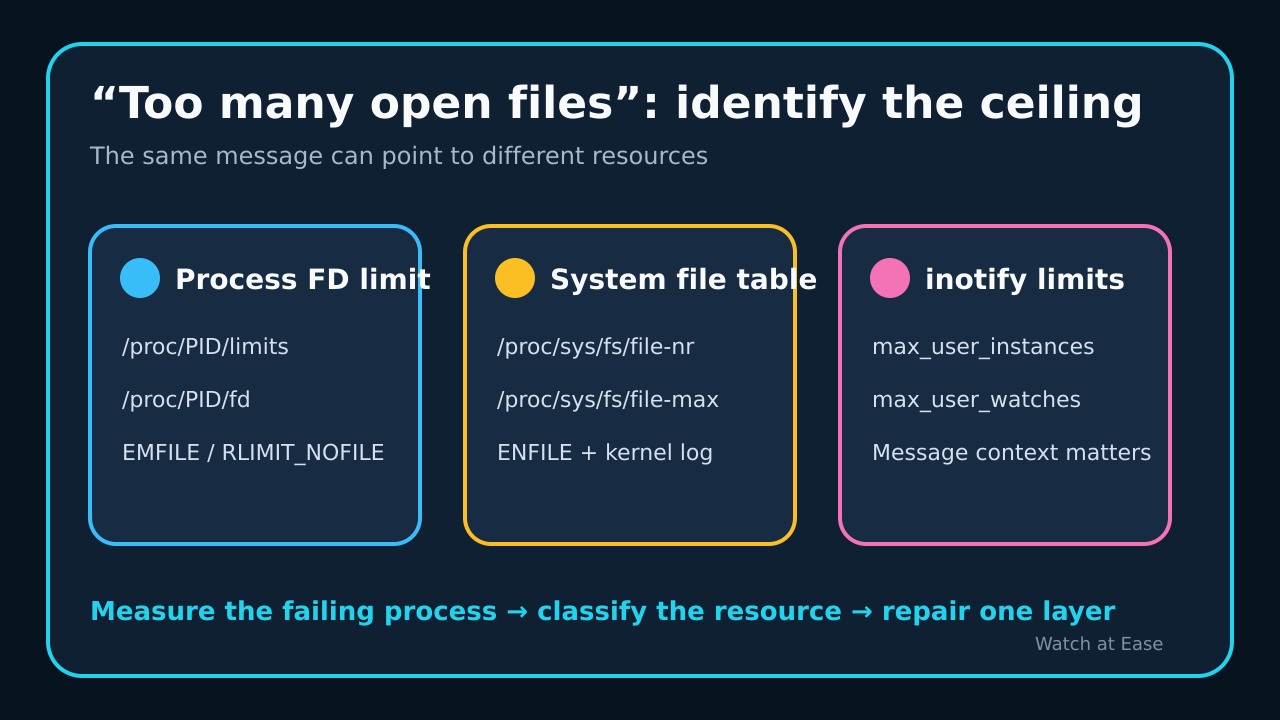
Original editorial diagram separating process file-descriptor, system file-table and inotify ceilings
Original conceptual illustration: the same message can require three different evidence paths. Watch at Ease
Technology · PRACTICAL GUIDE

Too many open files even after ulimit? Prove which Linux ceiling the service hit

A shell ulimit does not describe an existing service. Use the failing PID to separate RLIMIT_NOFILE, the system file table and inotify before changing any ceiling.
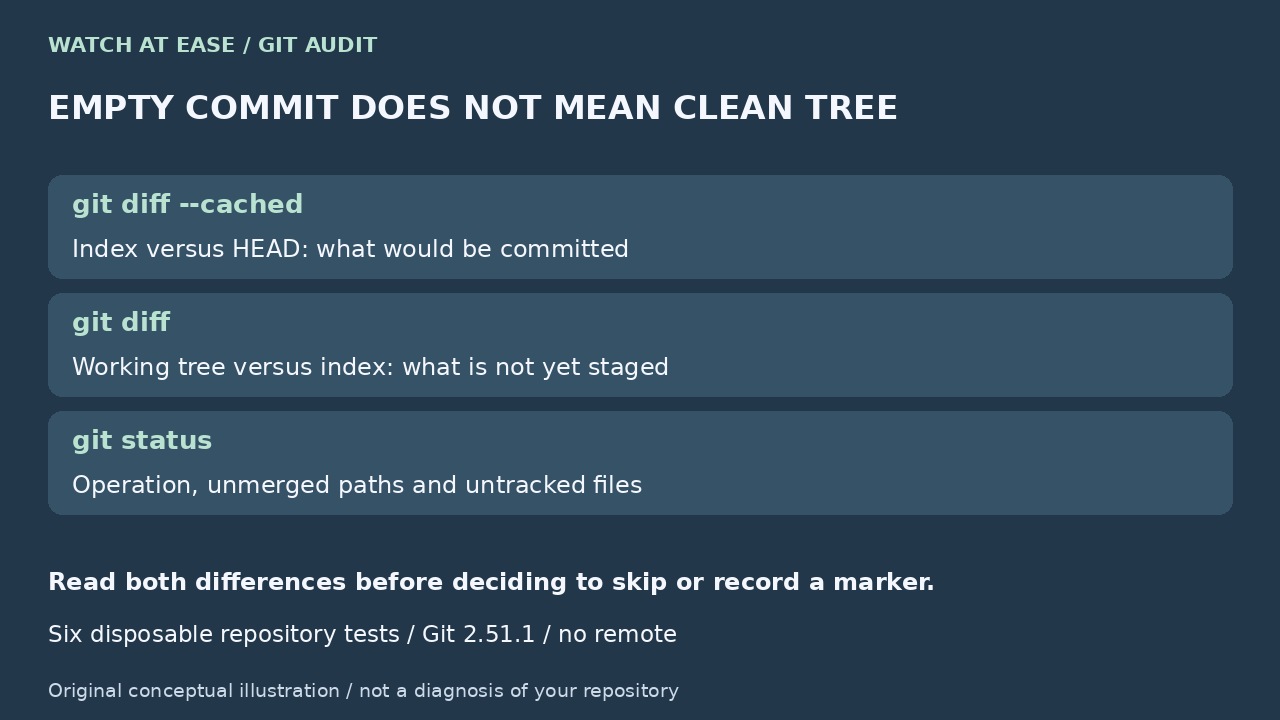
Original editorial illustration: Separate index and working-tree differences
Original conceptual illustration: An empty cached diff can coexist with wanted unstaged work; inspect both differences before choosing the policy. Watch at Ease
Technology · PRACTICAL GUIDE

Git says the cherry-pick is empty? Audit the index before skipping

An empty proposed commit is not proof that your working tree is clean or the fix is delivered. Six disposable Git tests show what to inspect before choosing skip, keep or drop.

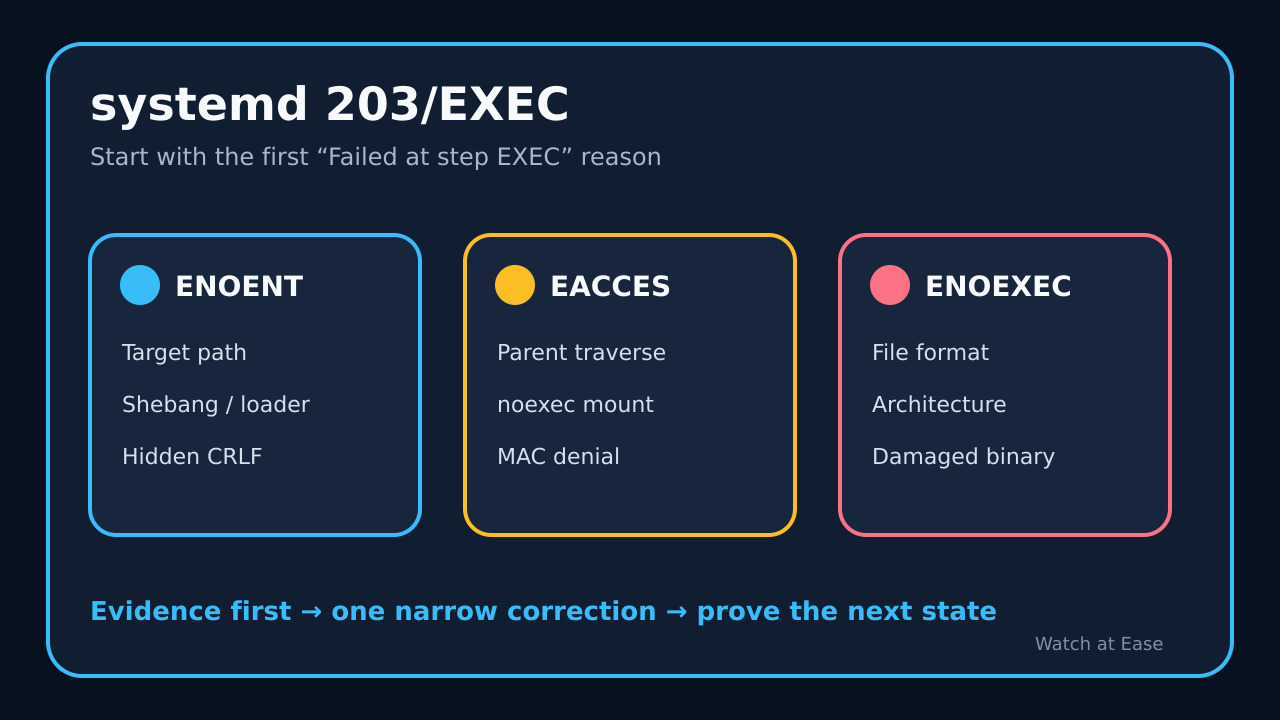
Original editorial decision tree separating systemd 203/EXEC by the journal reason
Original conceptual illustration: preserve the first EXEC line, then route ENOENT, EACCES and ENOEXEC to different evidence checks. Watch at Ease
Technology · PRACTICAL GUIDE

systemd status=203/EXEC? Audit the failed execve path before changing permissions

203/EXEC means the service manager could not execute the configured process. Use the exact journal message to separate a missing target or interpreter, invalid format, path or mount denial, and MAC policy before changing anything.

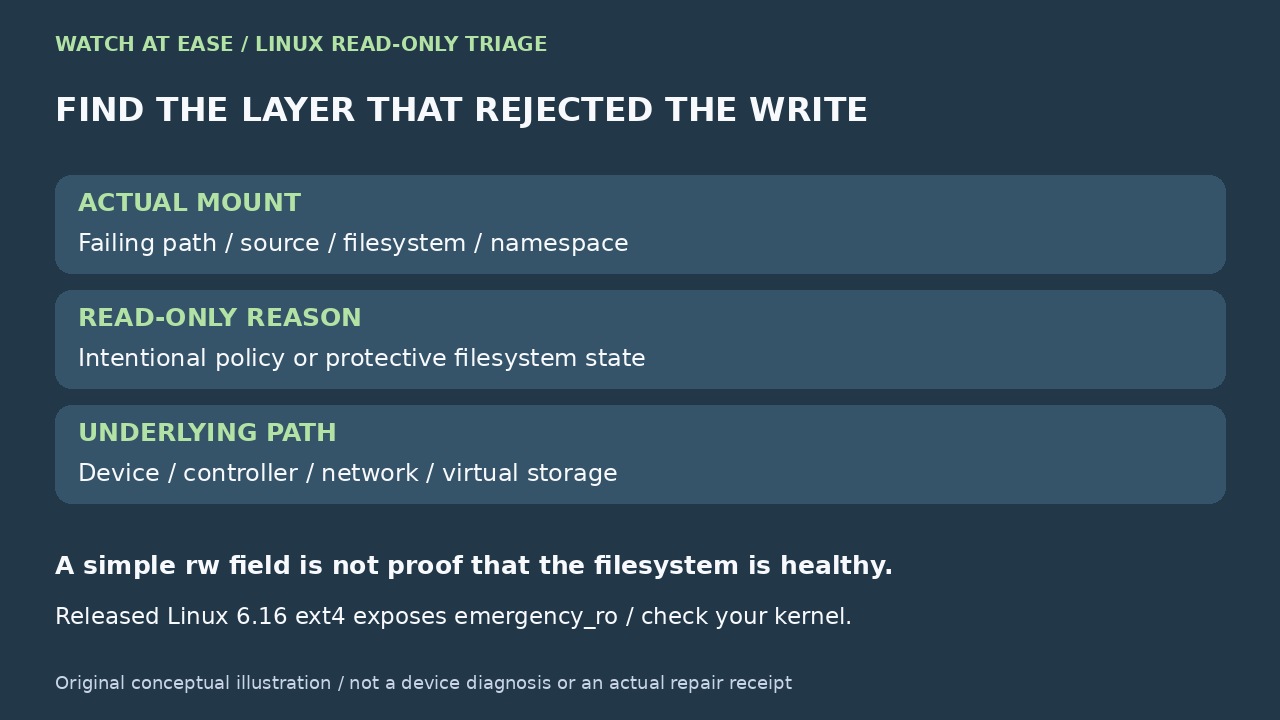
Original editorial illustration: Identify the read-only layer before attempting recovery
Original conceptual illustration: Map the real mount and distinguish policy, protective state and underlying storage; Linux 6.16 marker is version-specific, not a health guarantee. Watch at Ease
Technology · PRACTICAL GUIDE

Linux says “Read-only file system”? Diagnose the cause before you remount

The error may come from an intentional mount rule, a protective filesystem state, or a failing storage path. Identify the exact mount and preserve the evidence before you try to make it writable.

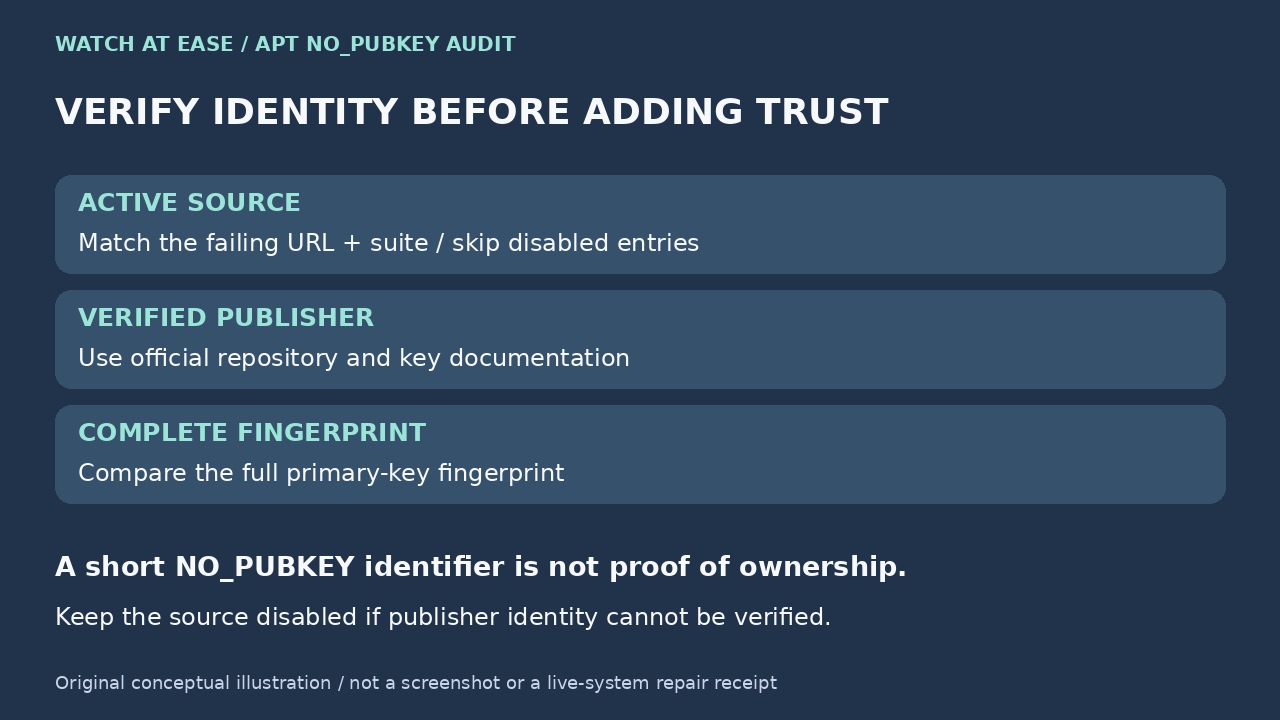
Original editorial illustration: Verify repository identity before trusting a key
Original conceptual illustration: Map the active source, verify the publisher, and compare the complete primary-key fingerprint; a short identifier is not ownership proof. Watch at Ease
Technology · PRACTICAL GUIDE

APT says NO_PUBKEY? Verify the repository and migrate its key without apt-key

Treat NO_PUBKEY as an identity and configuration failure, not a prompt to trust the first key you find. Map the error to one source, verify the publisher and full fingerprint, make the keyring readable to _apt, bind it with Signed-By, and prove that exact repository now verifies.

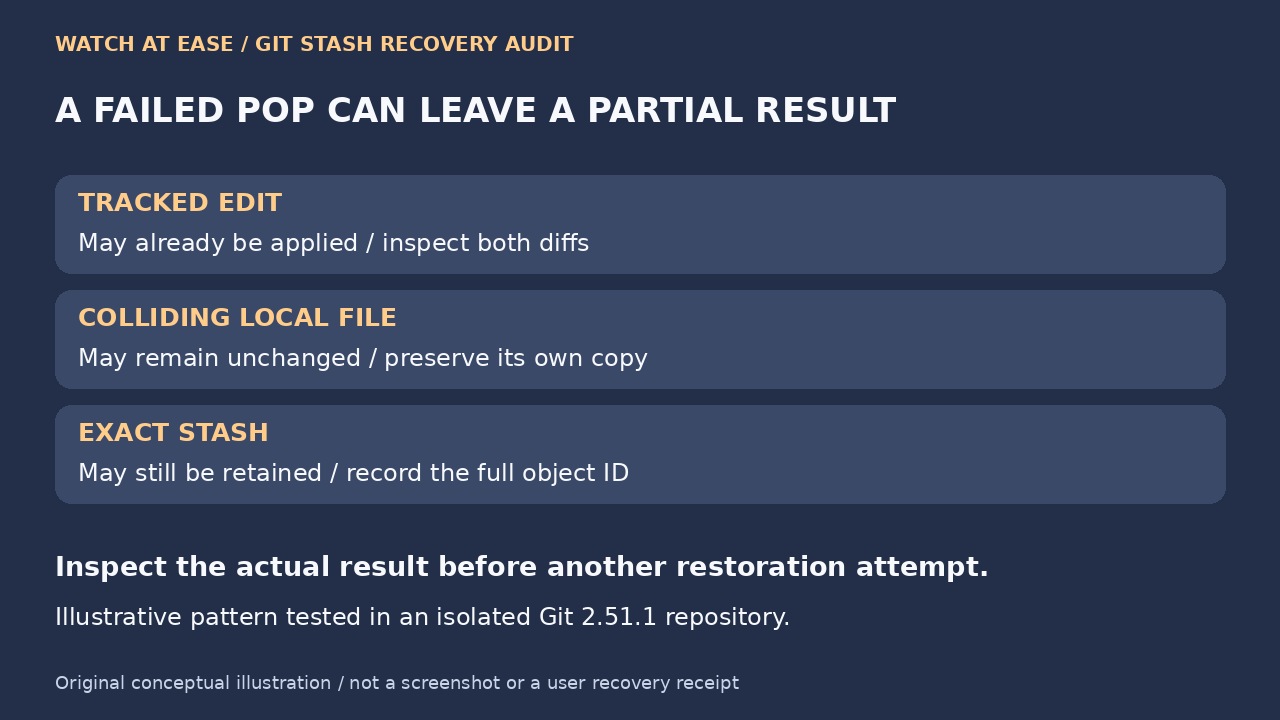
Original editorial illustration: A failed stash pop can leave a partial result
Original conceptual illustration: Tracked edits may already be applied while a colliding local file and the exact stash remain; inspect the actual result before retrying. Watch at Ease
Technology · PRACTICAL GUIDE

Git stash pop failed? Audit partial restoration before cleanup

A colliding file can block untracked restoration after tracked edits have already applied. Preserve both versions, identify the exact stash and compare the recovered result before deleting anything.

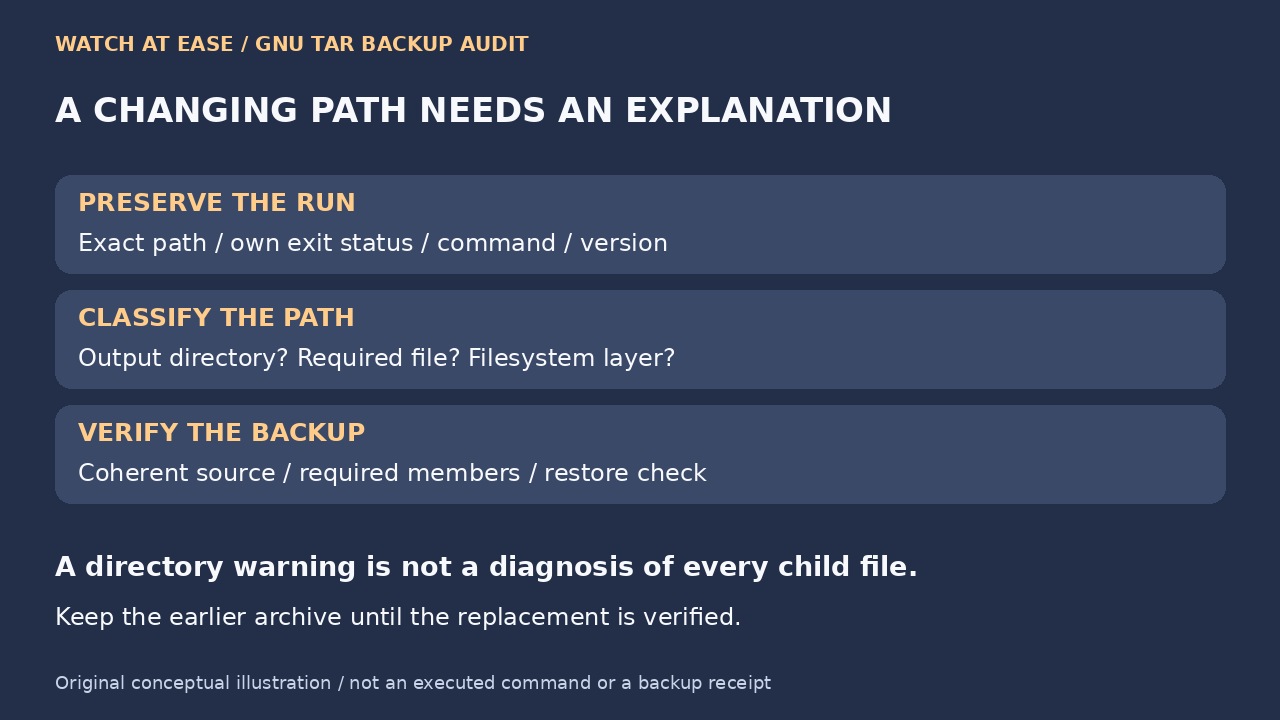
Original editorial illustration: GNU tar changing-path audit before backup acceptance.
Original conceptual illustration: The original diagram preserves the reported path and original status, classifies output/content/filesystem causes and checks coherent source, required members and restore use. Watch at Ease
Technology · PRACTICAL GUIDE

tar says “file changed as we read it”? Audit the changing path before suppressing the warning

Identify the exact path, preserve the original status and separate a changing directory from changing application data. A readable archive and a hidden warning are different from a backup you can restore.

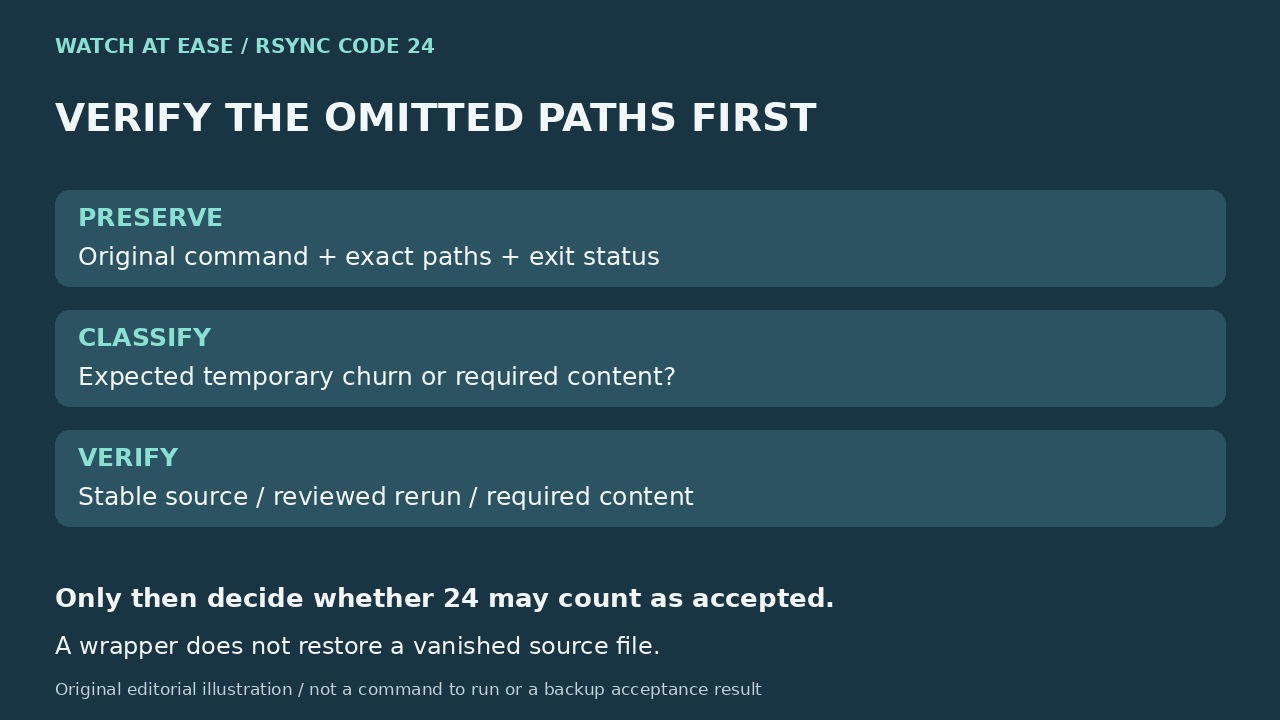
Original editorial illustration: Rsync code24 vanished-path audit before exit-code normalization.
Original editorial illustration: The original diagram preserves command/paths/status, classifies expected churn versus required content, and verifies a stable source and required data before acceptance. Watch at Ease
Technology · PRACTICAL GUIDE

Rsync code 24: audit vanished files before you ignore the warning

Exit code 24 means source files vanished during the transfer. Preserve the paths and original status, decide whether those files mattered, then verify a stable rerun before changing automation. An exit-code wrapper cannot turn omitted files into a complete backup.

Original editorial illustration of a person comparing an SSH warning fingerprint with a separate trusted server console.
Original conceptual illustration: Verify the server fingerprint through a separate trusted channel before changing the local trust record. Watch at Ease
Technology · PRACTICAL GUIDE

SSH says “REMOTE HOST IDENTIFICATION HAS CHANGED”? Verify the endpoint and fingerprint before removing the old key

Do not delete known_hosts or disable checking just to make the warning disappear. Identify the hostname, address, port, jump path and trust file SSH used; obtain the expected fingerprint through a separate trusted channel; then remove only the stale record after the fingerprints match.

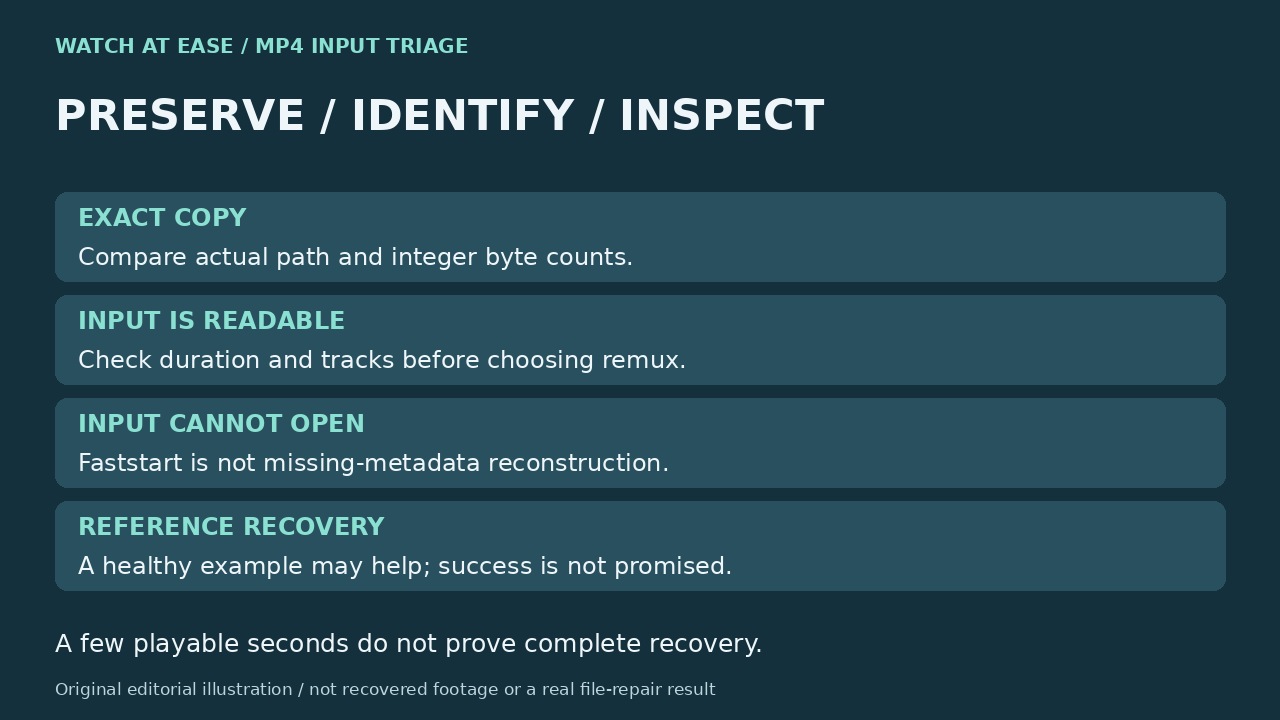
Original editorial illustration separating exact copy, readable input and missing metadata reconstruction.
Original editorial illustration: verify the copy and input first; not a recovery result. Watch at Ease
Technology · PRACTICAL GUIDE

“moov atom not found”: verify the copy before trying MP4 repair

Separate a different copy, an unfinished regular MP4 and a file that needs specialist reconstruction. Faststart moves an index; it does not restore an unreadable recording.

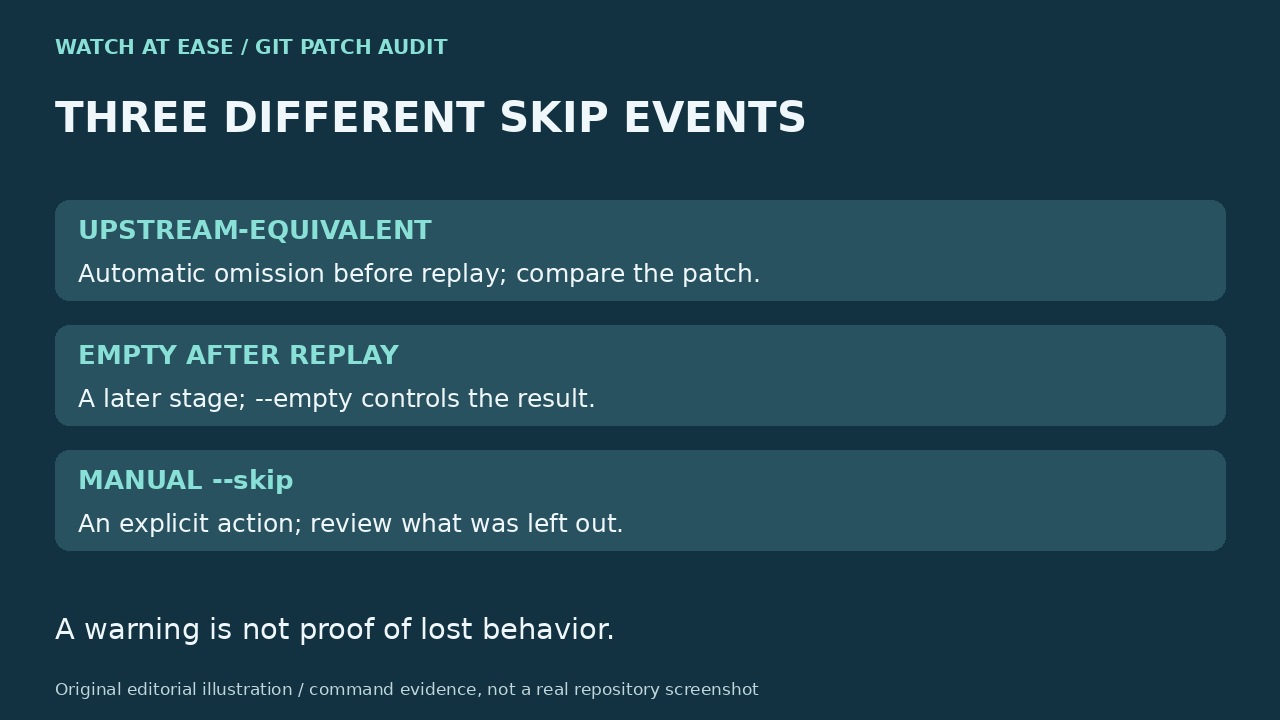
Original editorial illustration distinguishing upstream-equivalent omission, empty-after-replay and manual skip.
Original editorial illustration: inspect each stage separately; not a real repository screenshot. Watch at Ease
Technology · PRACTICAL GUIDE

Git rebase skipped a commit? Audit the patch before replaying it

A skipped commit hash does not prove lost code. Separate an upstream-equivalent patch, a commit that became empty, a manual skip and a GitHub merge restriction before rewriting history.

Original editorial illustration tracing a service unit through restart attempts to the first concrete failure.
Original editorial illustration: preserve the effective unit and earliest failure before clearing the rate counter. Watch at Ease
Technology · PRACTICAL GUIDE

systemd says “start request repeated too quickly”? Find the first failure before resetting

The final start-limit message is usually the guardrail, not the defect. Preserve the effective unit and earliest failed attempt, then repair the evidence-backed branch before clearing counters or changing retry limits.

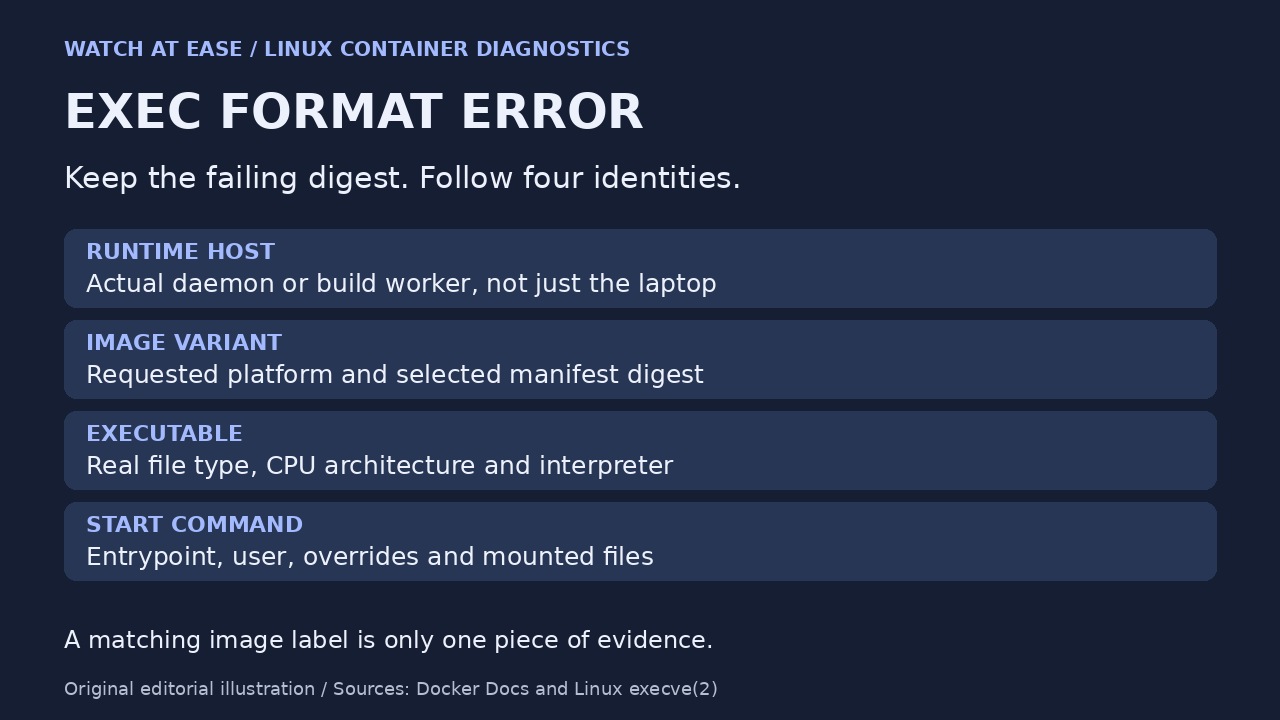
Original editorial illustration of runtime host, image variant, actual executable and start command evidence.
Original editorial illustration: preserve the failed digest and follow four linked identities; the image label is only one piece of evidence. Watch at Ease
Technology · PRACTICAL GUIDE

Docker says exec format error? Audit the image, binary and entrypoint before rebuilding

An exec format error is not a verdict that the image tag is wrong. Trace the selected manifest, final filesystem, executable architecture and entrypoint interpreter before pruning caches, adding QEMU or rebuilding blindly.

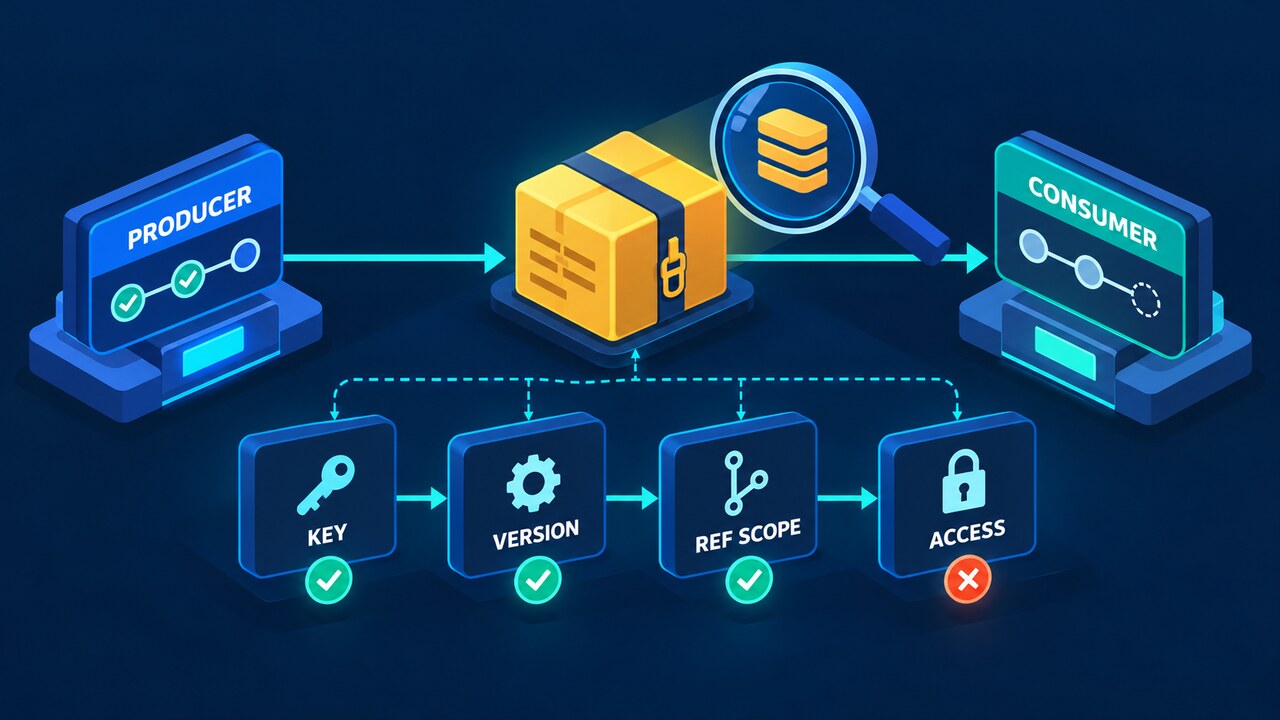
Original concept illustration comparing producer and consumer workflow runs across key, cache version, ref scope and access.
Original Watch at Ease concept illustration: a cache hit requires more than the visible key string. Watch at Ease / OpenAI-generated
Technology · PRACTICAL GUIDE

GitHub Actions cache not restoring? Audit key, version, scope and access before changing the runner

A cache entry can exist and still be invisible to the current run. Compare the producer and consumer across evaluated key, cache version, ref scope, access mode and entry state before deleting caches or changing runners.

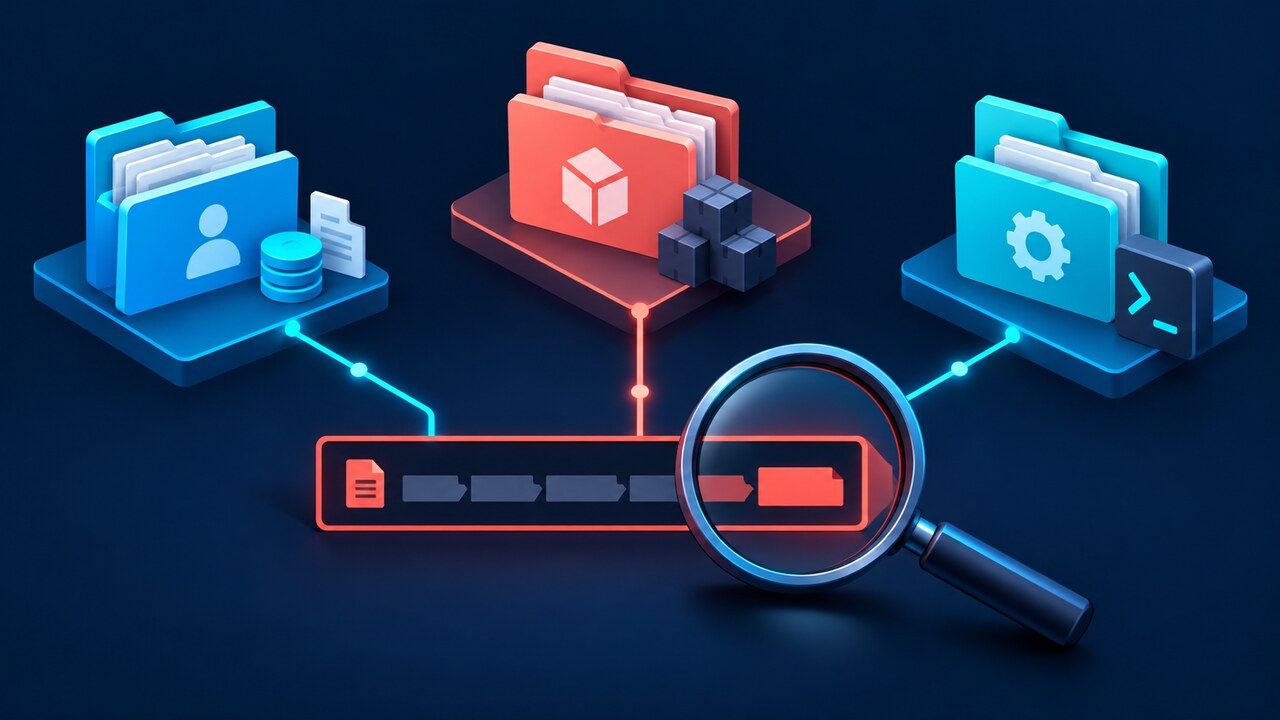
Original concept illustration showing three filesystem scopes connected to a magnified failing npm path.
Original Watch at Ease concept illustration: classify the exact denied path before changing ownership or permissions. Watch at Ease / OpenAI-generated
Technology · PRACTICAL GUIDE

npm EACCES permission denied? Read the failing path before sudo, chown, or prefix changes

Cache, project, global prefix, and container failures look alike but need different owners. Preserve the exact path and classify the scope before any mutation.

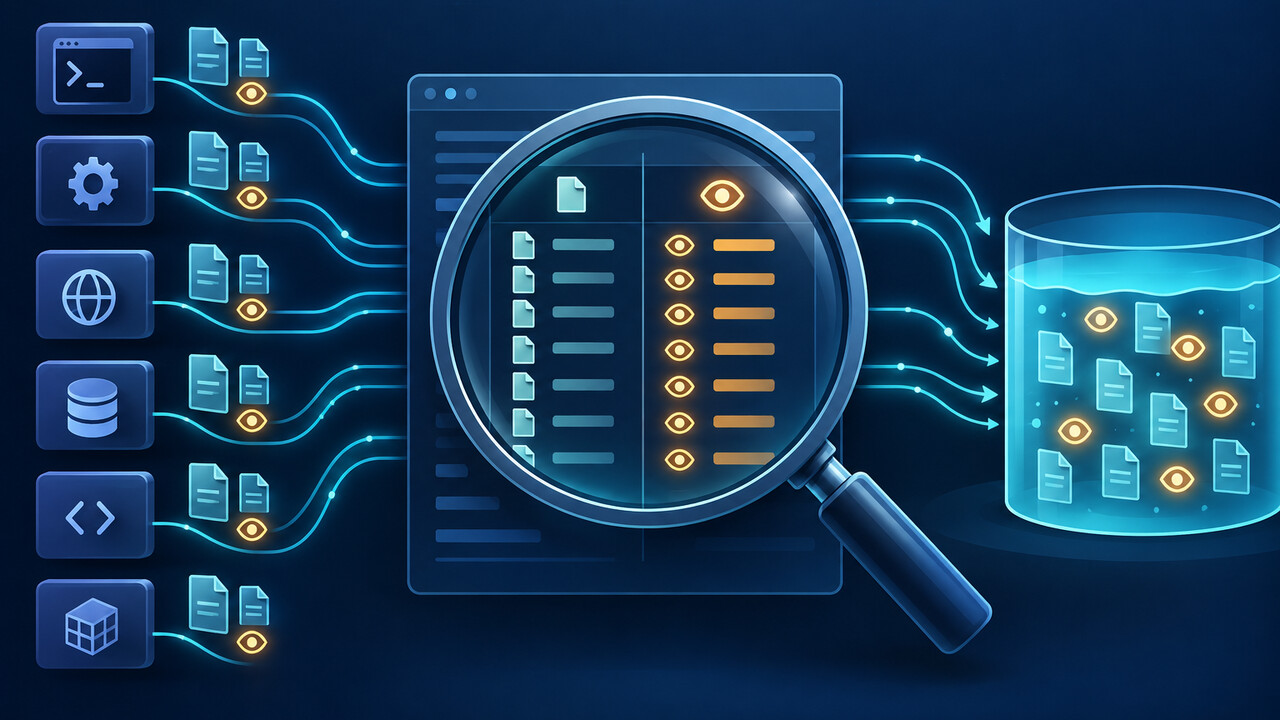
Original concept illustration of multiple process consumers, a read-only inspection ledger and a shared inotify resource pool.
Original Watch at Ease concept illustration: record instances, marks and visibility before choosing a next step. Watch at Ease
Technology · PRACTICAL GUIDE

ENOSPC says the file-watcher limit is reached? Build an inotify consumer ledger before raising sysctl

On Linux, the same ENOSPC message can hide exhausted watch marks, exhausted inotify instances, a broad watch scope, or another process using the shared per-user pool. Inventory consumers first, then change one limit or exclusion with evidence.

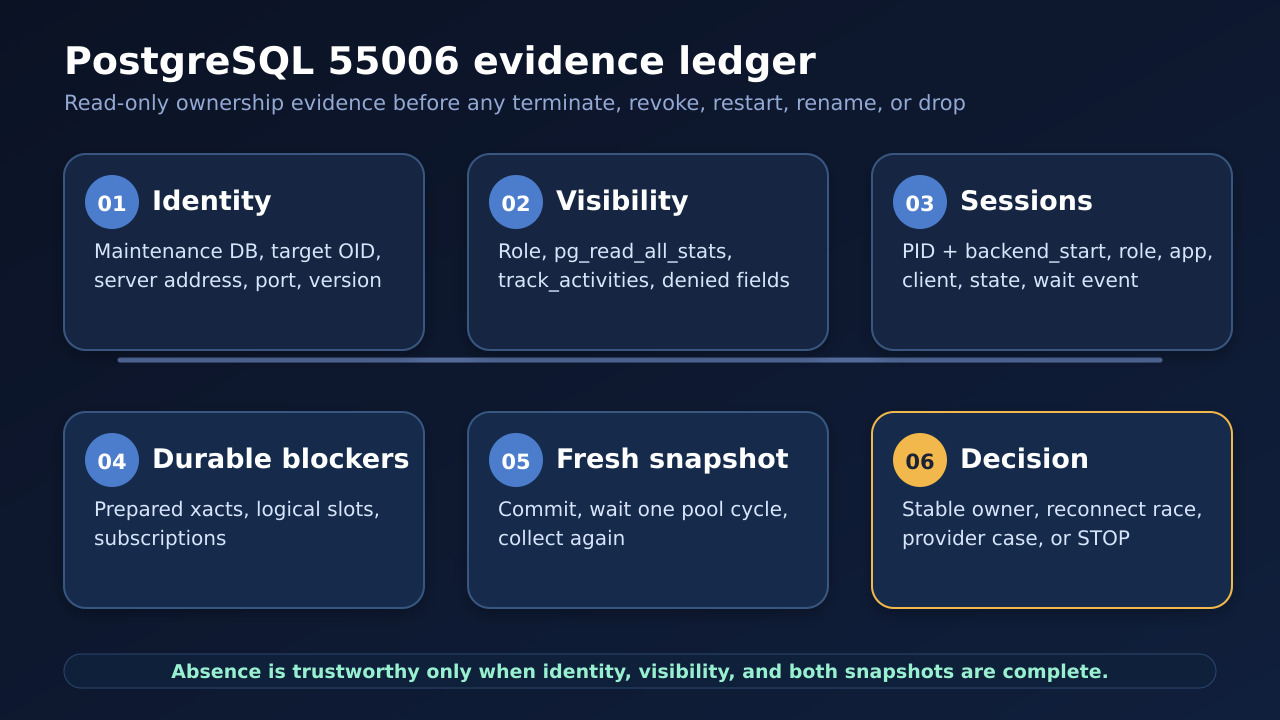
Six-step read-only PostgreSQL ownership ledger covering identity, visibility, sessions, durable blockers, a fresh snapshot and the decision boundary.
Original Watch at Ease concept illustration: a zero count is meaningful only when cluster identity, visibility and both snapshots are complete. Watch at Ease
Technology · PRACTICAL GUIDE

PostgreSQL says “database is being accessed by other users”? Build a session ledger before force drop

Do not make SQLSTATE 55006 disappear before you know who owns it. Capture a read-only, cluster-bound ledger of sessions, prepared transactions, logical replication objects and visibility limits, then repeat the snapshot to catch reconnect races before any destructive step.

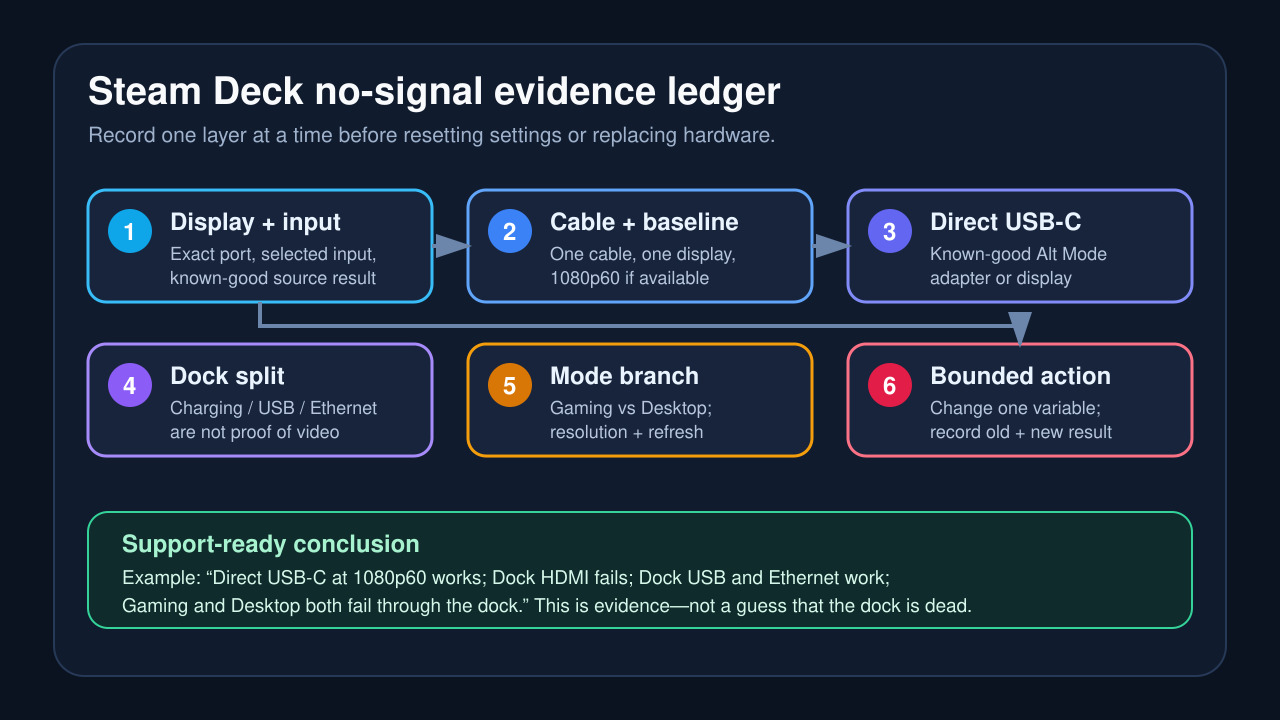
Six-step Steam Deck no-signal evidence ledger from display input through a bounded reversible action.
Original Watch at Ease concept illustration: record each display-path layer before changing settings or replacing hardware. Watch at Ease
Technology · PRACTICAL GUIDE

Steam Deck dock says no signal? Audit the display path before resetting anything

A no-signal message does not prove the dock is dead. Record which part of the display path still works, change one variable at a time, and keep mode-specific fixes on the correct branch.

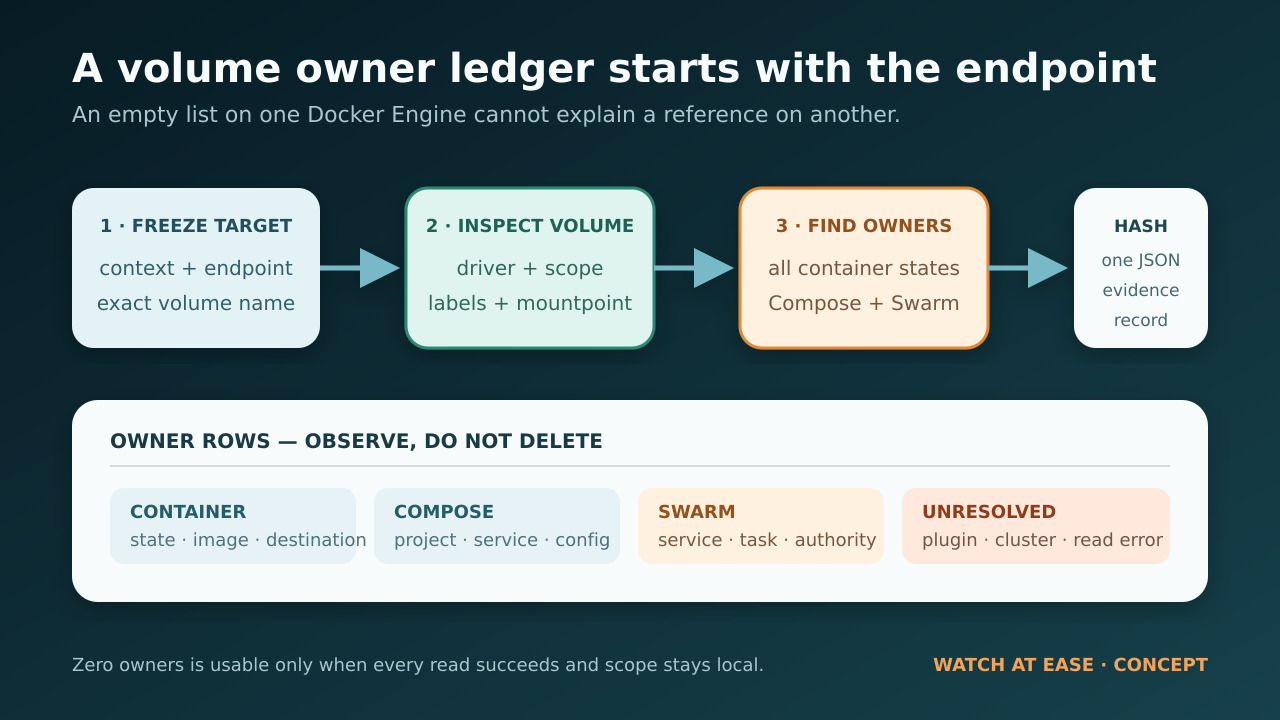
Original editorial diagram showing a Docker volume owner ledger built from the selected endpoint, volume metadata, container states, Compose labels and Swarm references.
Original editorial concept illustration: freeze the Docker context and endpoint, inspect the exact volume, inventory every owner, and preserve one hashed evidence record before cleanup. Watch at Ease
Technology · PRACTICAL GUIDE

Docker volume is “in use” but no container is obvious? Build an owner ledger before cleanup

Do not begin with --force, prune, or a daemon restart. Bind the error to the exact Docker context, inventory every mount owner—including stopped containers and Swarm services—and preserve the evidence first.

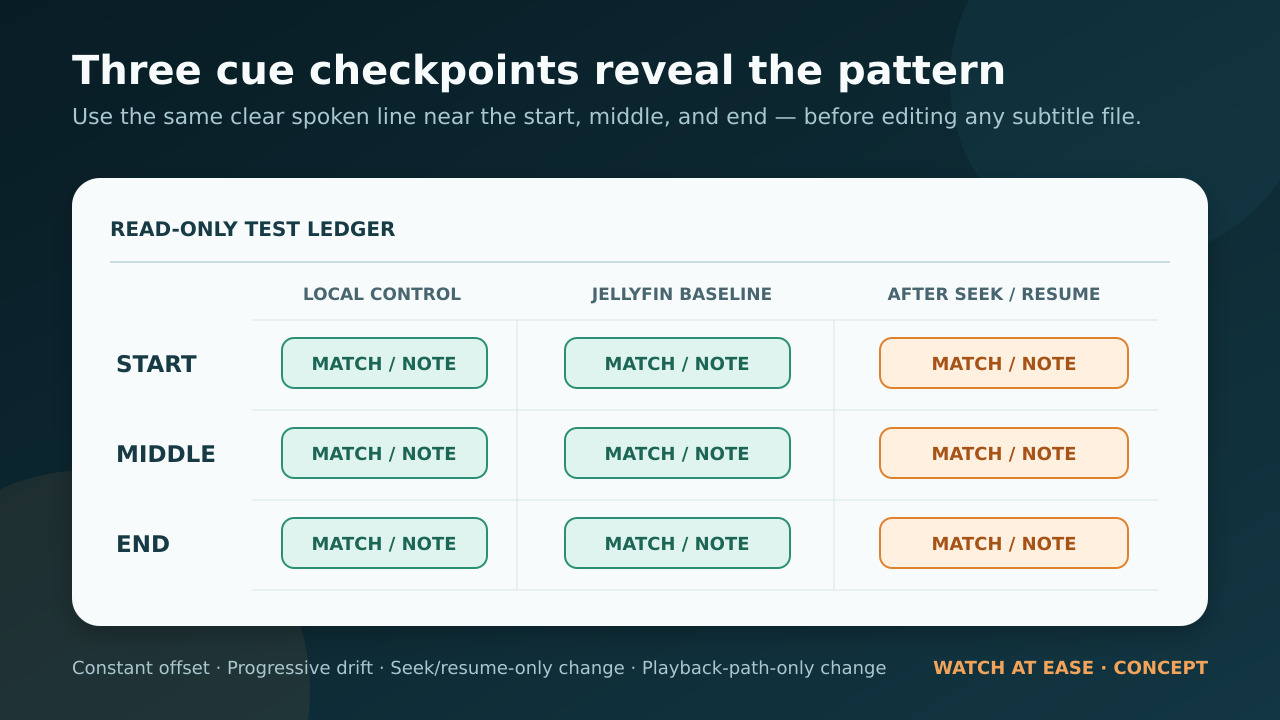
Original concept diagram comparing the same subtitle cues at the start, middle, and end
Original illustration: log the same three dialogue cues before changing any subtitle timing. Watch at Ease
Technology · PRACTICAL GUIDE

Jellyfin subtitles out of sync? Test the file, client, and playback path before retiming

A subtitle that drifts only after a seek, resume, direct stream, or transcode may not be a bad subtitle file. Preserve the original, test the same three dialogue cues across local and Jellyfin playback, and record the path that creates the mismatch before you edit anything.