Technology · NEWS EXPLAINER
SBI investigates dark-web exposure after 3,897 customer records show personal data
The bank distinguished a roughly 375,000-record dataset from 3,897 records containing personal information and said its core operations remained unaffected.
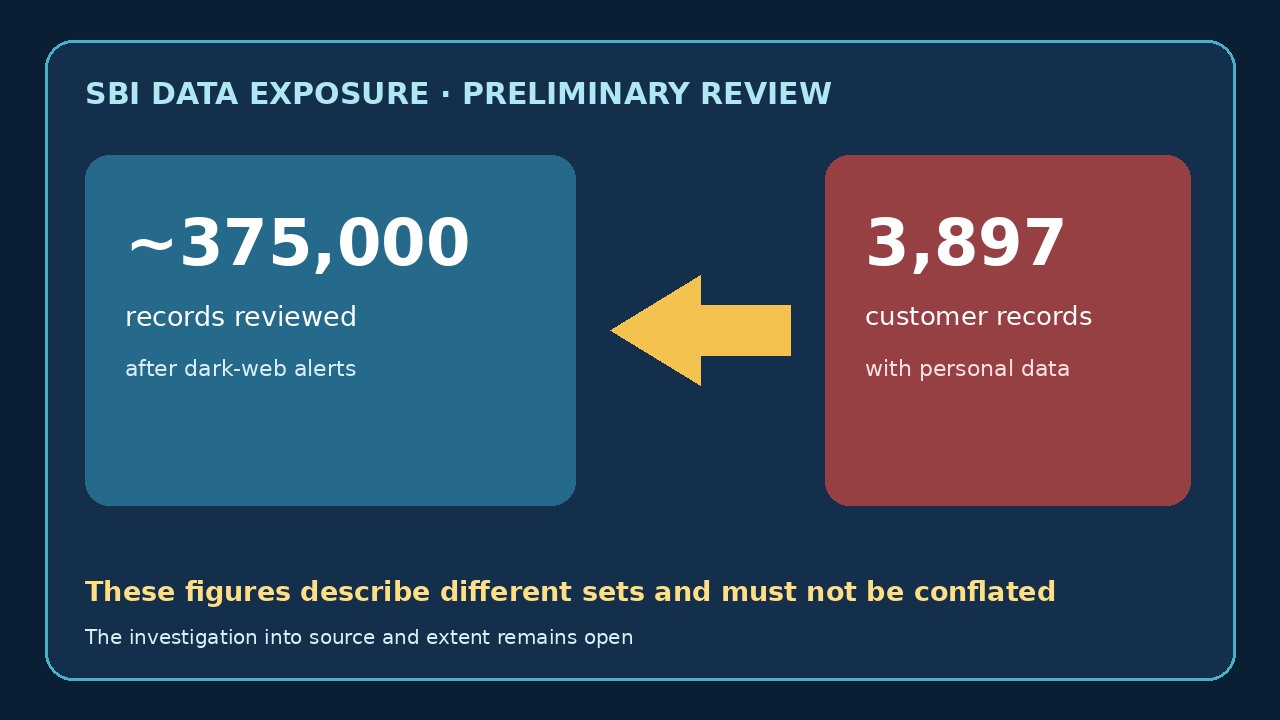
State Bank of India said a preliminary review of roughly 375,000 records found on the dark web identified 3,897 customer records containing personally identifiable information.
SBI activated incident-response procedures and appointed an independent cybersecurity agency, while saying the incident had no material effect on core operations, financial performance or business continuity.
A preliminary review identified 3,897 records with personal information
SBI said roughly 375,000 records were available on the dark web. Its preliminary analysis identified 3,897 customer records containing personally identifiable information. The larger figure is the reviewed dataset; it is not the number of customers confirmed as affected.
The exposed fields went beyond names and phone numbers
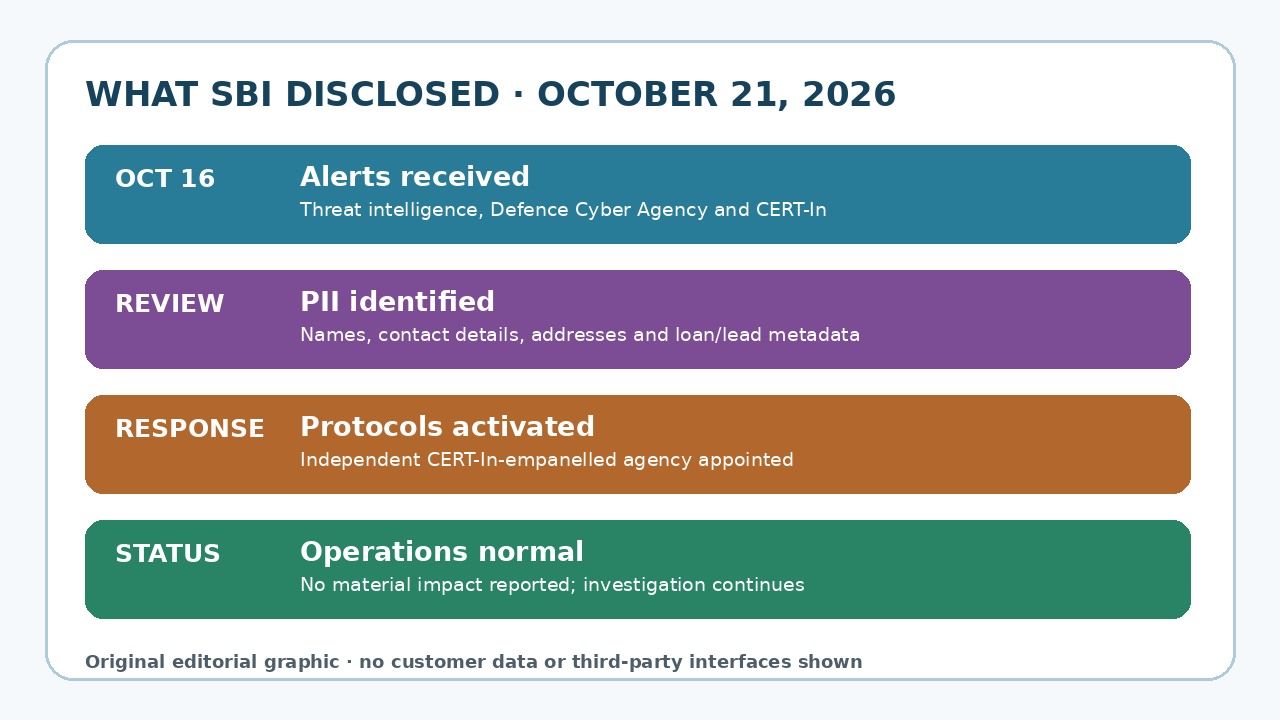
The identified records included names, registered mobile numbers, dates of birth, gender, email and residential addresses, branch and Customer Information File identifiers, lead IDs, and metadata associated with loan or lead records. The bank has not published the individual records.
Alerts arrived on October 16 and the source is still being investigated
Indian Express reported that SBI received alerts from its threat-intelligence provider, India’s Defence Cyber Agency and CERT-In on October 16. SBI activated its incident-response and containment procedures and engaged an independent CERT-In-empanelled cybersecurity agency to determine authenticity, source and extent.
SBI reported normal operations, but the assessment is not finished
The bank said it did not expect a material impact on core operations, financial performance or business continuity. That operational statement does not close the investigation or establish how the data reached the dark web; both the source and full scope remain under assessment.