Technology · PRACTICAL GUIDE
PostgreSQL says current transaction is aborted? Find the first error before retrying
Treat SQLSTATE 25P02 as evidence of an earlier failure: preserve the first SQLSTATE, prove the connection and transaction owner, then choose full rollback or a savepoint that existed before the risky work.
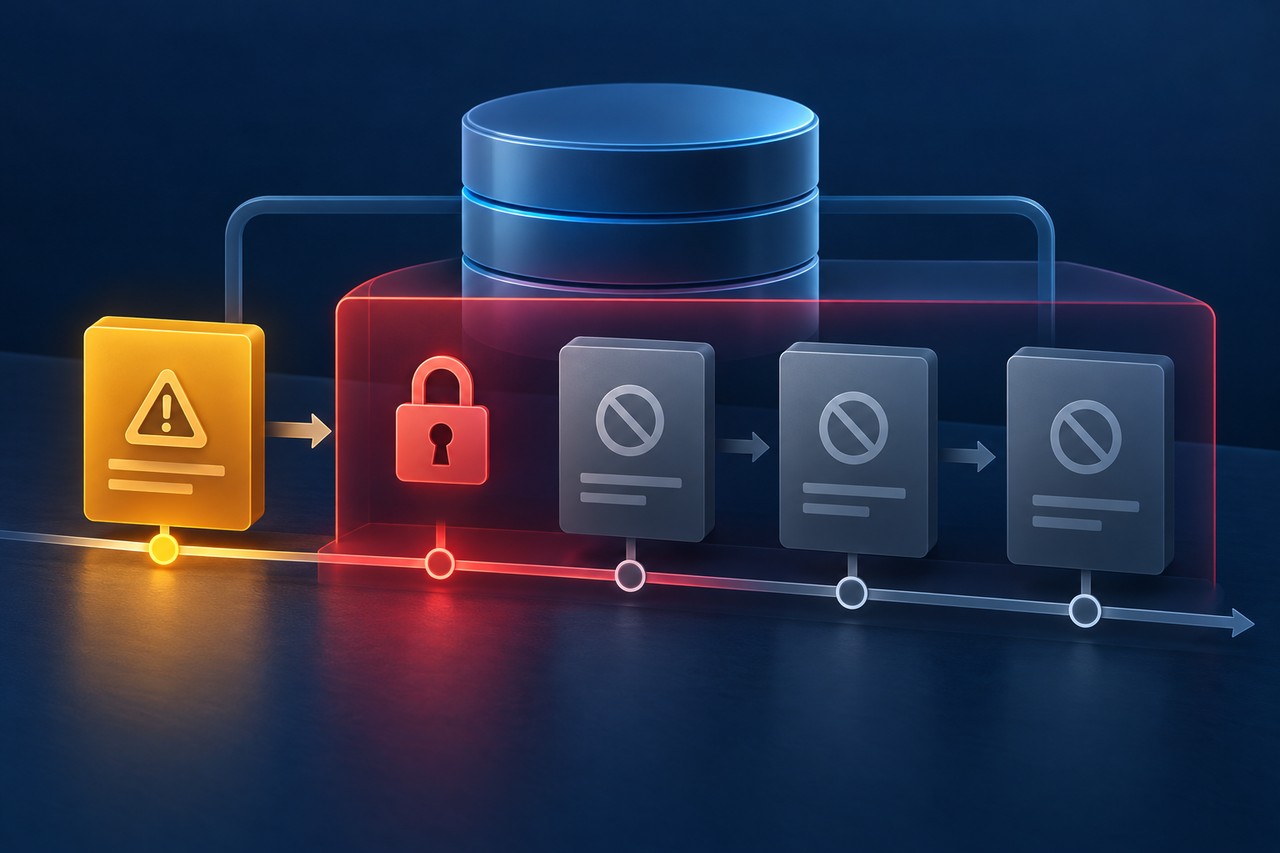
PostgreSQL’s “current transaction is aborted” message is usually the aftermath of an earlier statement failure. Repeating the last command cannot repair the transaction and may hide the original evidence.
The safe sequence is to capture the first error, map it to one connection and transaction owner, choose the narrowest valid recovery, and verify the connection before retrying or returning it to a pool.
Freeze the first failure before you recover
SQLSTATE 25P02 means a statement earlier in the same transaction failed and PostgreSQL is ignoring later commands until the transaction is recovered. The repeated message is usually an echo, not the first cause. Preserve the earliest server error, its SQLSTATE, statement name or safe fingerprint, parameters classification, timestamp and stack trace before issuing rollback or retry.
Do not paste secrets or full personal data into an incident note. A statement fingerprint, request ID and parameter types are usually enough to join application logs to database logs. If the first visible line is already 25P02, widen the log window and inspect client-generated statements, triggers, constraint errors and earlier exceptions on the same connection.
Prove the exact connection and transaction boundary
Record the application instance, pool name, connection identifier, database, user, backend process ID when available, autocommit setting and transaction start time. The same request may cross several connections, while one pooled connection may serve many requests. Without that mapping, a later 25P02 can be attributed to the wrong query.
Identify who opened the transaction: explicit BEGIN, an ORM unit of work, a migration framework, a notebook cell, a database client, or an implicit driver transaction. Psycopg starts a transaction even for a SELECT by default unless autocommit is enabled, so an apparently read-only step can define the boundary that later code inherits.
Use a full rollback when no safe savepoint exists
If the transaction can be abandoned, call the driver or framework rollback operation and verify the connection is no longer in a failed transaction before retrying. In Psycopg, rollback is required before the same connection can be used again after an operation fails. Returning an aborted connection to a pool without cleanup turns one request’s failure into another request’s symptom.
Rollback removes every uncommitted change in that transaction. Before doing it in an interactive repair or migration, record what work will be lost and whether the application owns the whole transaction. Do not issue COMMIT to make the error disappear; an aborted transaction cannot preserve the failed unit as a successful commit.
Use a savepoint only if it existed before the risky work
A savepoint can preserve earlier work only when it was established before the statement that failed. Recover with ROLLBACK TO SAVEPOINT, then either continue deliberately or release the savepoint after the transaction is usable again. Creating a savepoint after 25P02 is already visible is too late.
PostgreSQL does not allow RELEASE SAVEPOINT while the transaction remains aborted; ROLLBACK TO is the recovery command inside the block. If a driver or framework created the savepoint, use its transaction context or documented API so internal state stays synchronized with the server.
Audit pools, ORMs and database clients for hidden statements
Check whether health checks, row-count probes, metadata queries, callbacks or automatic flushes ran before the SQL shown in the user interface. The DBeaver issue is useful demand evidence precisely because a client-generated statement preceded the error the user thought they were testing. Treat it as a branch to investigate, not as proof your client has the same bug.
For a pool, define the return rule: commit or rollback deliberately, verify idle state, then release. For an ORM, preserve the first database exception before higher-level error wrapping. For a notebook or GUI, start a fresh transaction only after the old connection state is understood; opening a new tab can hide the poisoned session without explaining it.
Retry the unit, not the final statement
After rollback, fix the original cause first: syntax, constraint, serialization, permission, type, timeout or client-generated SQL. Then retry the smallest idempotent business unit from its defined boundary. Retrying only the last INSERT or SELECT can duplicate earlier side effects outside the database or run with assumptions that the rollback invalidated.
Classify retryability by the first SQLSTATE, not 25P02. A deterministic constraint violation needs corrected input; a transient concurrency error may support a bounded retry; a permission error needs configuration. Keep an idempotency key or reconciliation check when the request also called another service, sent a message or wrote a file.
Verify a clean connection before returning it to service
Run a harmless state check through the same framework path and confirm the next transaction begins and ends normally. Inspect pool reset logs or connection status rather than assuming the absence of a new exception proves cleanup. If the driver discards the connection, record that replacement separately from a successful rollback.
Close the incident with the first SQLSTATE, the transaction owner, connection identity, recovery branch, lost work, retry decision and prevention change. Useful prevention includes shorter transaction scopes, explicit context managers, savepoints around expected optional failures, and logging that keeps the first database exception attached to the request.