기술 · 실용 가이드
OpenSSL wrong version number? TLS를 바꾸기 전에 port, protocol, proxy 경로를 증명하세요
정확한 경로와 첫 bytes를 보존하고 plaintext, 잘못된 port, HTTP proxy, STARTTLS, inspection 또는 framing 손상을 분리합니다.
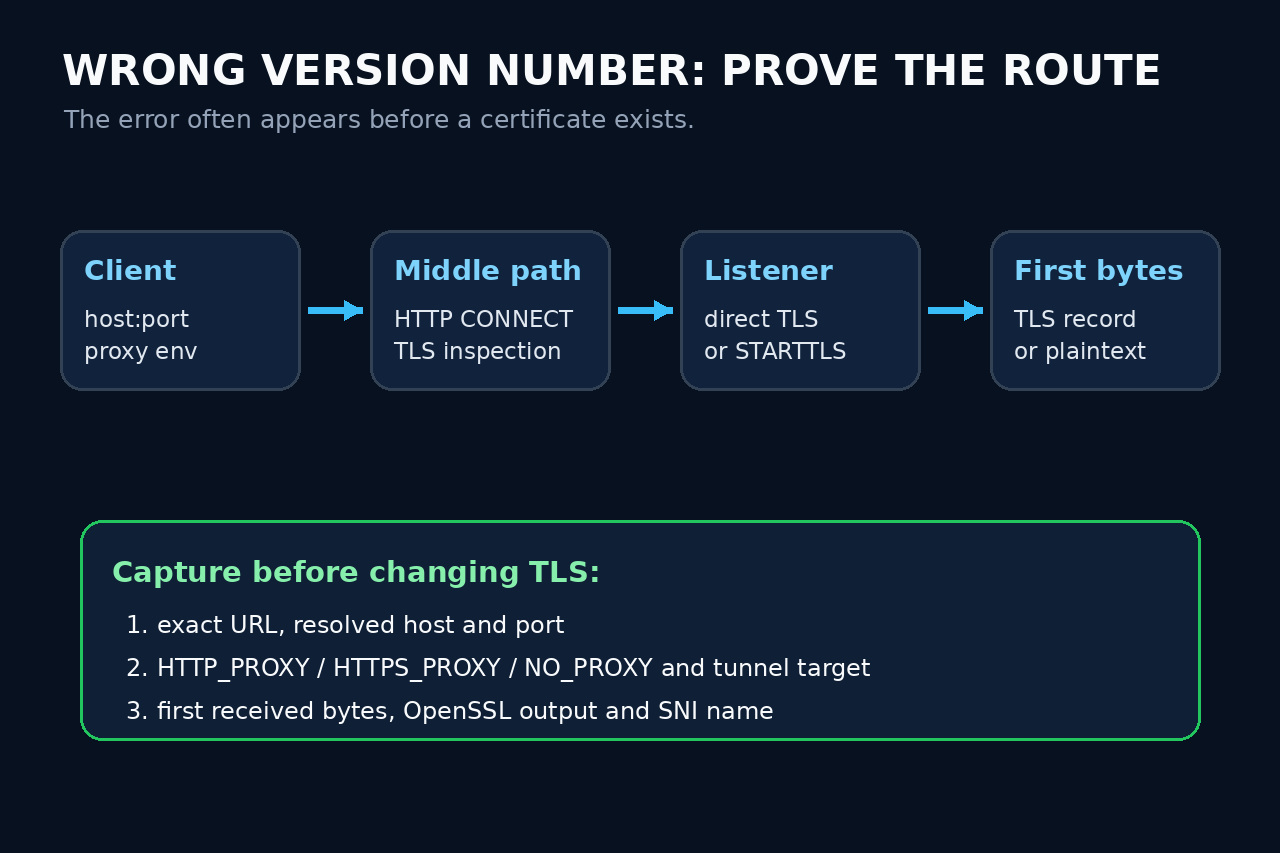
wrong version number는 record-layer 단서이며 상대가 오래된 TLS만 지원한다는 증거가 아닙니다. certificate가 오기 전에 first bytes가 TLS record 모양이 아니어서 발생할 수 있습니다.
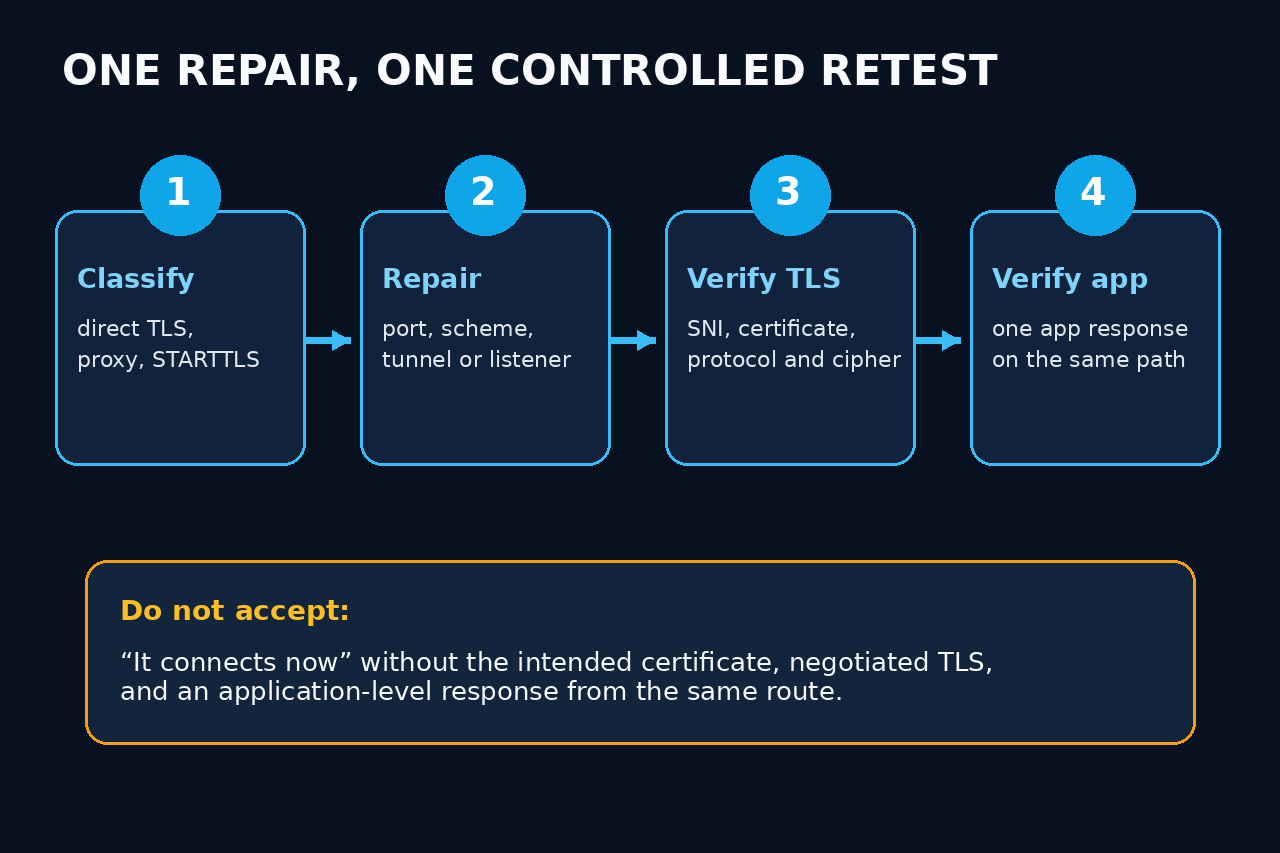
URL, host, port, proxy 환경과 error를 보존하고 direct TLS, HTTP CONNECT 또는 올바른 STARTTLS로 같은 경로를 검사합니다. 한 경계만 고치고 TLS identity와 application response를 승인합니다.
정확한 경로와 첫 실패를 고정합니다
application, OpenSSL version, URL, resolved address, port, proxy variables, NO_PROXY, mesh 또는 inspection device를 기록하고 retry 전에 first failure를 보존합니다.
peer certificate가 없고 몇 bytes만 읽었다면 trust store보다 protocol boundary를 먼저 확인합니다. secret이 담긴 capture는 공개하지 않습니다.
direct TLS, CONNECT, STARTTLS를 분류합니다
immediate TLS는 openssl s_client -connect host:port -servername host -brief로 검사하며 IP에 연결해도 SNI는 목표 virtual host를 사용합니다.
HTTP proxy는 -proxy로 CONNECT하고 endpoint가 plain HTTP일 수 있습니다. mail, LDAP, PostgreSQL 등은 맞는 -starttls를 사용합니다.
첫 response를 protocol evidence로 읽습니다
TLS record에는 정의된 header와 handshake가 있습니다. HTTP status, SMTP banner, proxy block page나 error word는 TLS endpoint 앞의 component가 응답했다는 증거입니다. 짧은 redacted sample을 보존합니다.
wrong listener, reverse proxy port, health endpoint, sidecar, outbound proxy, inspection gateway 또는 application protocol owner로 매핑합니다. network별 차이는 route 차이입니다.
증명된 경계만 수리합니다
scheme, port, proxy/CONNECT policy, STARTTLS, load balancer listener, upstream mapping 또는 framing 중 증명된 하나를 고칩니다. 오래된 TLS나 verification off로 숨기지 않습니다.
first bytes가 TLS이고 later negotiation이 실패하면 alert, version, cipher, certificate, SNI의 별도 사건으로 처리합니다.
같은 경로에서 TLS와 application을 승인합니다
원래 runtime과 path에서 certificate identity, hostname verification, protocol, cipher, SNI, proxy/STARTTLS와 remote address를 기록하고 application verification을 유지합니다.
마지막에 harmless application response 하나를 얻습니다. 옛 error가 사라진 것만으로 승인하지 말고 route ledger를 보존합니다.