科技 · 實用指南
NGINX 回報 upstream sent too big header?放大 buffer 前先確認協定與 response header 所有者
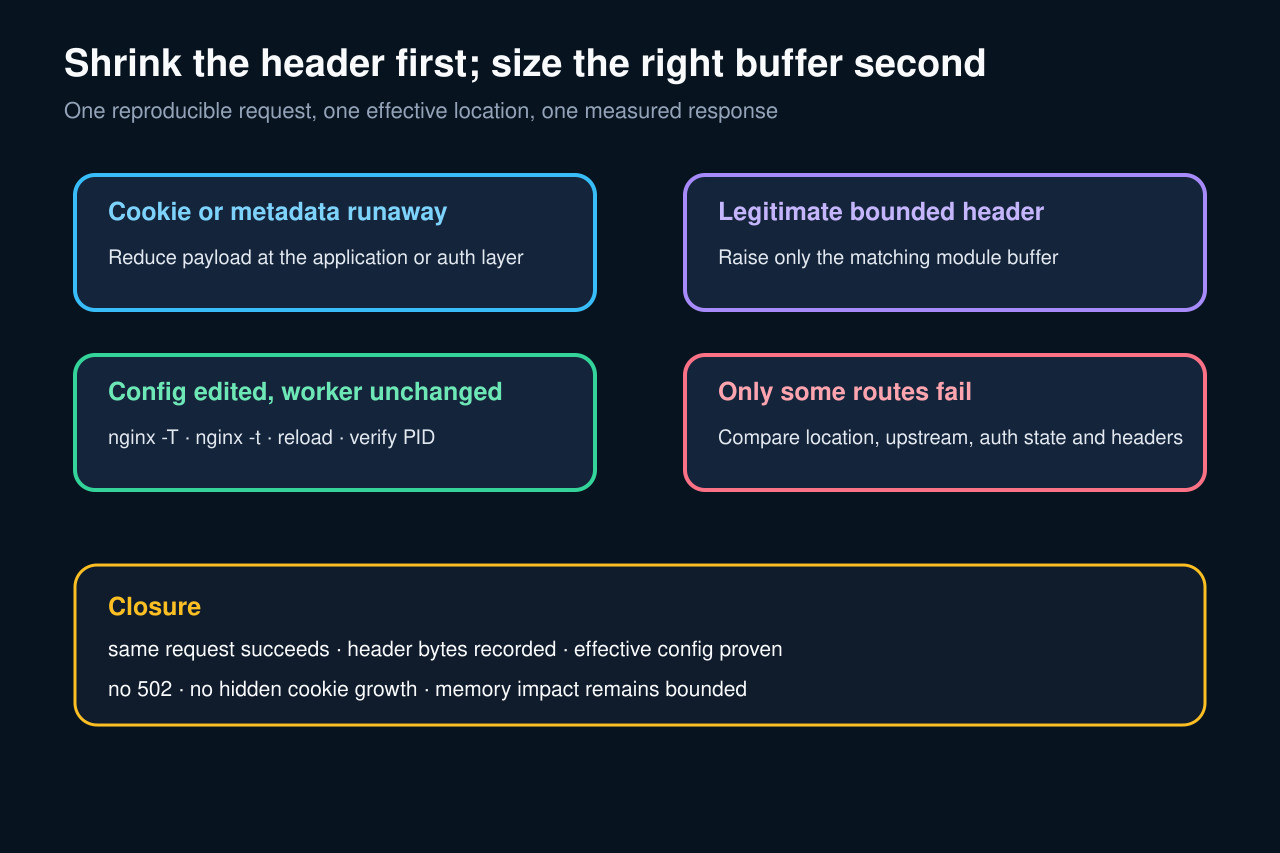
證明 route 使用 proxy、FastCGI 或 uWSGI,量測真實 response headers,縮小失控 Cookie 或 metadata,再只調整故障的 first-response buffer。
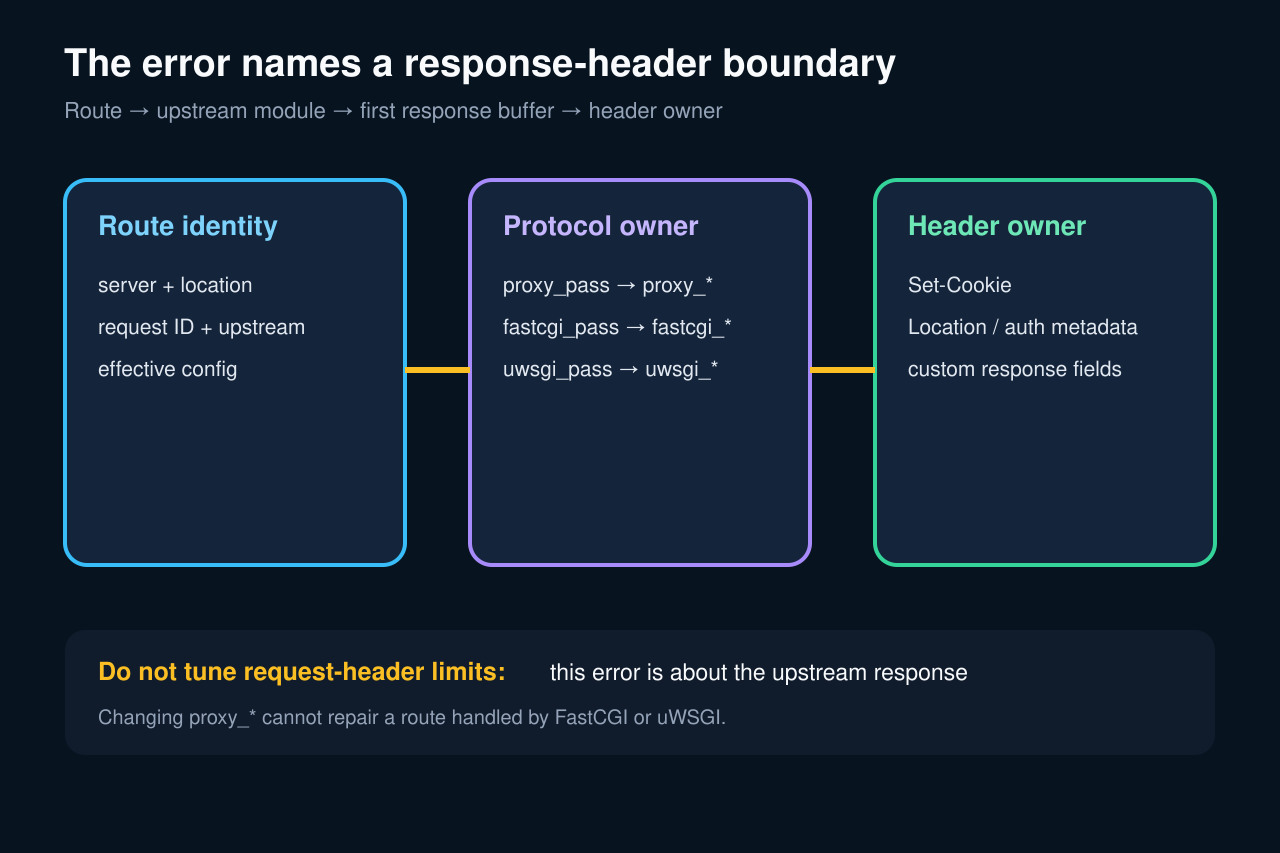
此錯誤屬於 upstream response header,不是 upload body 或 client request-header limit,也不證明所有 buffers 都應放大。
保存一個失敗 request、列印有效 location、確認 module、量測 header bytes 並縮小異常欄位;確有合理上限時才調整對應 buffer。
保存失敗 request 並列印有效 route
保存完整 NGINX error、timestamp、request ID、host、URI、status、upstream address 與 worker PID。用它關聯 access、upstream application 與 authentication logs,但不要記錄 Cookie 等秘密值。
在實際執行的相同 image 或 host 上執行 nginx -T,保存 include 展開後的 server 與 location。記錄 master PID、config path 與 deployment revision;修改未被 worker 載入的檔案不算修復。
選擇指令前確認 upstream protocol
錯誤來自 upstream response。location 使用 proxy_pass 時檢查 proxy_buffer_size;fastcgi_pass 與 uwsgi_pass 各自有不同 directive family。client_max_body_size 與 large_client_header_buffers 屬於 request-side boundary。
根據 error log 的 upstream scheme 與 effective location 選擇指令,不要套用通用片段。proxy_* 無法改變由 FastCGI 或 uWSGI 處理的 request,全域放大也可能不必要地提高每條 route 的記憶體。
量測 response-header owner
在安全環境或直連 upstream path,以相同 authentication 與 session state 重現。記錄 header 名稱與 byte length 並遮蔽值,特別檢查重複 Set-Cookie、Location、auth metadata 與 custom fields。
比較成功與失敗 response,判斷是單一 field 超過 first-response buffer,還是多個 fields 累積。若成長來自 session、OAuth state 或 serialized application data,應優先在產生端修復。
實施最小 module-specific 變更
縮小重複或過大的 Cookie,把大型 session state 移到 server side,移除不必要 metadata 並限制 redirect/auth state。合法 header 仍較大時,只在最窄 effective context 提高對應 module buffer。
調整 proxy buffering 時維持 proxy_buffers 與 busy-buffer constraints,但不能取代 first response header 的量測。先做 syntax check,再 graceful reload,並確認 running worker 已載入展開後設定。
以相同 state 重跑並確認 bounded memory
重播相同 URI、method、upstream、authentication callback 與 session size。確認不再出現 502、error log 乾淨且 application result 正確,再測試 near-limit 與 over-limit case。
記錄新舊 directives、effective location、header-byte summary、worker reload time、request ID、concurrency、memory impact 與 rollback threshold。持續監控 login 或 cart 增長後的 headers,避免新 buffer 只是延後無界成長。