Technology · PRACTICAL GUIDE
curl error 77? Prove which CA file or directory failed before replacing certificates
Error 77 means curl could not read the selected CA certificate location. Identify the binary, TLS backend, override and effective path; then test traversal, bytes and store structure before repairing one input and retesting without insecure mode.
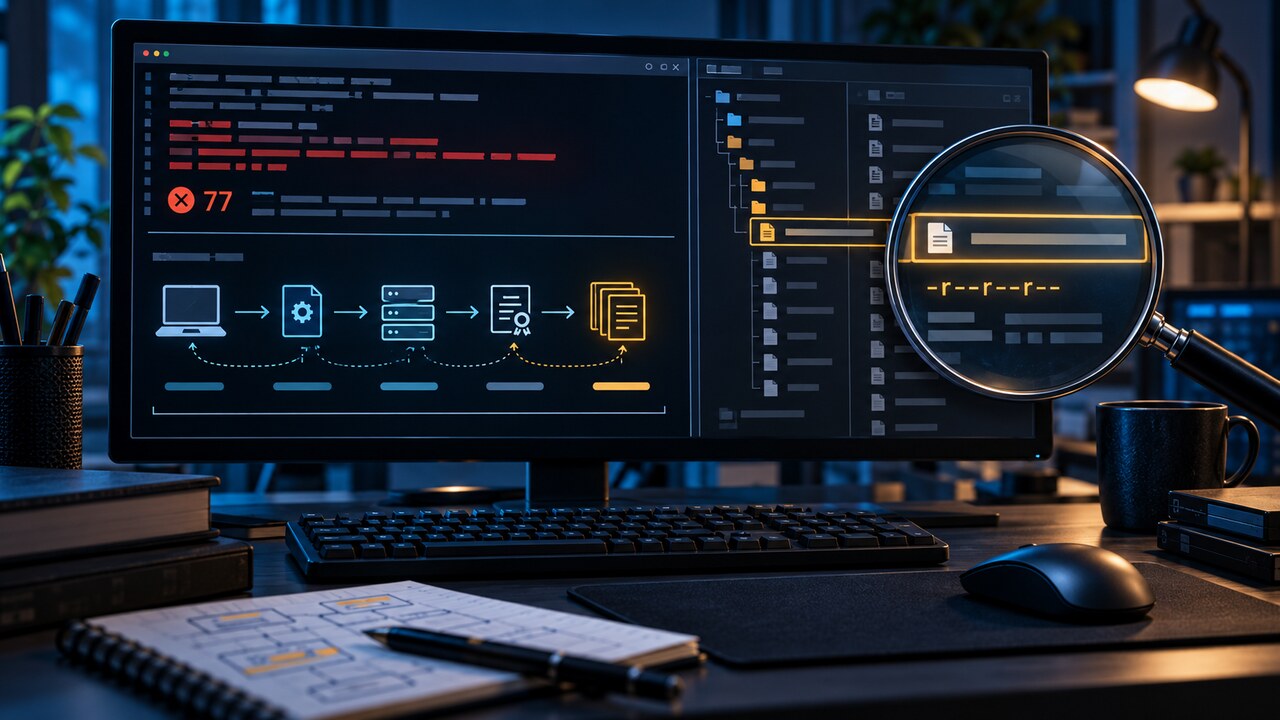
curl error 77 is a local trust-store loading failure, not proof that the remote server certificate is bad. The official curl reference narrows it to reading the SSL CA certificate location.
Do not start by using --insecure, chmod 777 or downloading an arbitrary bundle. First prove which curl binary and TLS backend ran, which file or directory it selected, and why that exact location cannot be loaded.
1. Capture the exact failing runtime
Record the executable path, curl version and TLS backend, the redacted command, exit code, working directory, user or service identity, container image and wrapper. A shell curl, PHP extension, Python binding and application-embedded libcurl can load different builds and configuration.
Capture the full error line and verbose startup output with credentials removed. Do not publish Authorization, Cookie, signed query parameters, client keys or internal hostnames. The CAfile and CApath printed by the failing process are evidence, not suggestions.
2. Resolve option and environment precedence
List explicit --cacert or --capath settings, application configuration, CURL_CA_BUNDLE, SSL_CERT_FILE and SSL_CERT_DIR, then compare them with the compiled default shown by the actual build. Test inside the same service, container or CI step; an interactive shell may have a different environment.
Change nothing yet. Put the selected input and its source in a table: command option, wrapper setting, environment variable, platform-native store or compiled default. If two layers disagree, remove only the unintended override and rerun one controlled request.
3. Prove path traversal and file identity
As the failing user, inspect every directory component and the final object. A readable file is insufficient if a parent directory cannot be traversed, a symlink resolves outside a sandbox, a bind mount is absent or a security policy blocks the target. Record the resolved path, owner, mode, size, digest and mount or container boundary.
Do not use chmod 777 as a diagnostic shortcut. It changes more permissions than necessary and cannot repair an absent mount, empty bundle, wrong file type, malformed PEM or denied sandbox path. Restore the intended ownership and least-privilege access after identifying the boundary.
4. Validate CAfile or CApath structure
For CAfile, reject a directory, PKCS#12 archive, zero-byte file or HTML download masquerading as a certificate bundle. OpenSSL expects PEM certificate blocks and processes the file when loading the verification locations. Parse a copy with OpenSSL tooling before replacing a system-managed bundle.
For CApath under OpenSSL, certificate files must use the hashed lookup layout; run the platform-appropriate rehash tool on the intended directory and inspect the generated links. A directory full of PEM files without the required names can still fail to supply certificates when needed.
5. Repair one layer and close with a secure test
Repair the narrow cause: remove a stale override, restore the package-managed bundle, correct the mounted path, replace an empty artifact from the trusted distribution source, fix the PEM input or rebuild the hashed directory. Preserve the old file and package logs when corruption or image construction is under investigation.
Retest with the same runtime and destination, without --insecure. Require exit code 0, a verified TLS connection, the intended CA source and no fallback to an unexpected bundle. Then test the real wrapper or service and record the corrected path, owner, bytes, digest and configuration source for future builds.