Technology · NEWS EXPLAINER
California begins notifying families after student data was copied from an ETS file-transfer site
The incident may affect current and former public-school students. California says copied records can include names, addresses, disability information and test data, while Social Security numbers and financial-account information were not involved.
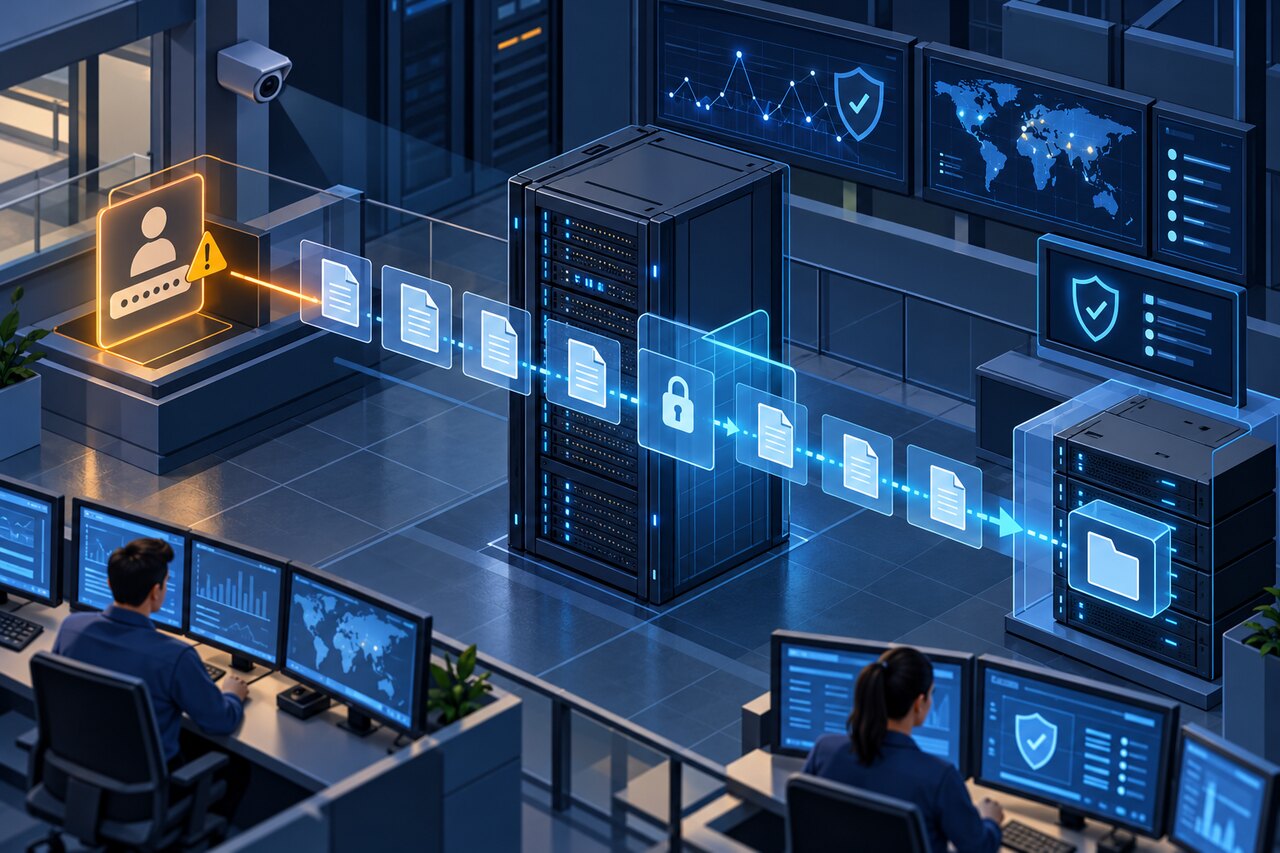
California has begun notifying students and families after an intruder used a compromised login credential to copy files from a transfer site operated by Educational Testing Service. The state says the exposed fields vary by person and is offering affected current and former students two years of identity-protection service.
What California disclosed
California's education department said Educational Testing Service began notifying students and families on October 16 after an investigation found that an unauthorized party copied files from an ETS-operated secure file-transfer site. The account involved was disabled and the site was taken offline. Notifications are expected to continue through early November, so a family may not receive a letter immediately even if a student is affected.
Who may be affected
The state's incident page says the copied information includes, but is not limited to, records for all students enrolled during the previous three school years. It also says affected people can include current and former California public-school students enrolled from 2023 through the current school year, plus some students who left a California school as far back as 2006 without a confirmed transfer. More than 5.7 million students were enrolled in the 2025–26 school year alone, but officials have not published one final count of unique affected individuals.
The data involved—and what was not
Information varied by person and may include names, dates of birth, residential addresses, schools, districts, grade levels, state or local student identifiers, demographic details, language and program participation, disability or accommodation information, and statewide assessment data. The official notice says Social Security numbers, financial-account information, passwords, and parent or guardian information were not involved. ETS says its monitoring had found no evidence, as of the notice, that the copied information had been made public; that is not a guarantee that it will never be misused.
How the access happened
ETS identified unauthorized activity on September 25. The investigation determined that someone used a compromised login credential to access the file-transfer site and copy files at various times from May 22 through September 18, 2026. CDE says the site exchanged statewide assessment information used for programs including CAASPP and ELPAC. Officials have not publicly identified the intruder or explained how the credential was compromised.
What families can do now
Use the California Department of Education incident page as the starting point rather than links in unsolicited messages. It links the official notice in 27 languages and lists the incident phone line, 833-931-8488, open Monday through Friday from 6 a.m. to 6 p.m. Pacific time. ETS is offering affected current and former students two years of Experian IdentityWorks service at no cost; the state page provides separate enrollment paths and engagement numbers for minors and adults. Families that have not received a letter can still review the official FAQ, keep contact information current with the relevant school or district, and watch for communications that match the official details.
What has changed—and what remains open
ETS says it took the affected site offline, built a new transfer site with stronger controls, increased monitoring and access controls, and added third-party security review. California's cybersecurity integration center is assisting with forensics and incident response, while state education officials are reviewing the incident and ETS's contractual security compliance. The public record still leaves important questions unresolved, including a final person count, whether every copied field can be mapped to each student, and whether law enforcement will identify a responsible party.