Technology · NEWS EXPLAINER
BT launches a UK-managed Sentinel security service: check who can act, and when
BT’s expanded Microsoft partnership adds a managed security operations offer. Buyers still need to establish response authority, covered systems and the handling of their data.
BT announced a UK-managed security operations centre service for Microsoft Sentinel on October 13 as part of an expanded partnership with Microsoft. The offer combines Microsoft’s security platform with BT’s operational expertise, threat intelligence and network insight for UK businesses and public-sector organisations.
For a buyer, the useful question is what the managed service actually takes responsibility for. A platform name and an operating location do not, by themselves, specify which systems are monitored, who may contain an incident or how quickly someone will act. Those details need to be established for the proposed deployment.
The new offer builds on an existing relationship
BT describes the launch as a further step in its strategic relationship with Microsoft. It already had a role as a managed service provider for Sentinel, so the news should not be read as BT discovering security operations for the first time or Sentinel becoming an entirely new technology. The material development is the announced UK-managed SOCaaS offer within that expanded partnership.
The release promotes a more proactive approach to threats and potential improvements in protection, efficiency and cost. These are the suppliers’ statements about the offer. The announcement is not a comparative test of detection accuracy, a contractual response-time commitment or proof that an organisation will avoid every attack.
Separate the platform from the operating agreement
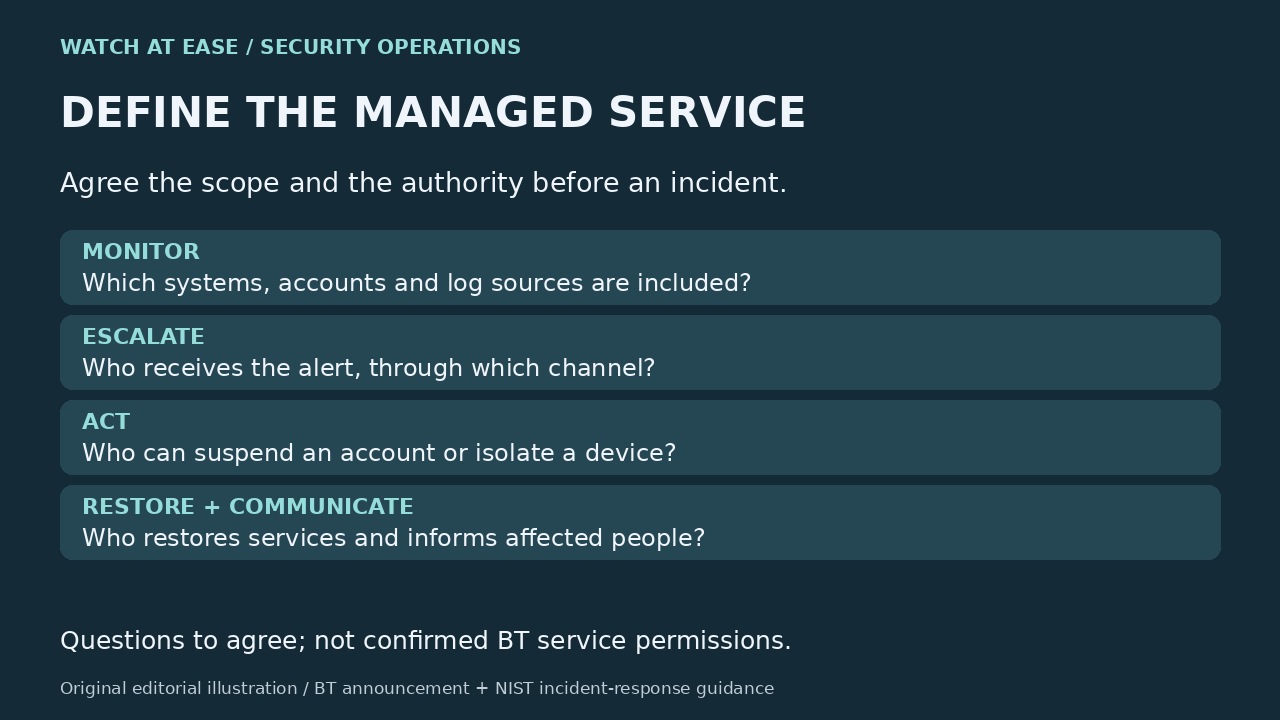
Sentinel is the named platform; SOCaaS is the security operations service layered around it. Before assessing a proposal, ask for a precise list of the systems, accounts and log sources included, the onboarding work required, and what happens when a required source stops sending information. A service can only be evaluated against an agreed scope.
Also establish how alerts reach your own team and what authority the provider has after escalation. Can it suspend an account or isolate a device, or must it obtain approval first? These are editorial procurement questions, not features or permissions confirmed in BT’s announcement.
Outsourcing still needs a clear division of work
NIST’s April 2025 incident-response guidance provides an independent framework for this issue. Section 2.2 says third-party responsibilities should be defined in a contract, including information flows, coordination and authority to act. It also notes that a provider’s privileged access and access to sensitive data introduce risks that need attention.
That guidance is background, not an endorsement of BT or a judgment that this service satisfies UK requirements. Applied here, it suggests documenting who detects, who approves disruptive action, who restores services and who communicates with affected people. The customer and supplier should have a shared account of that division before an incident tests it.
Ask for evidence behind location and performance claims
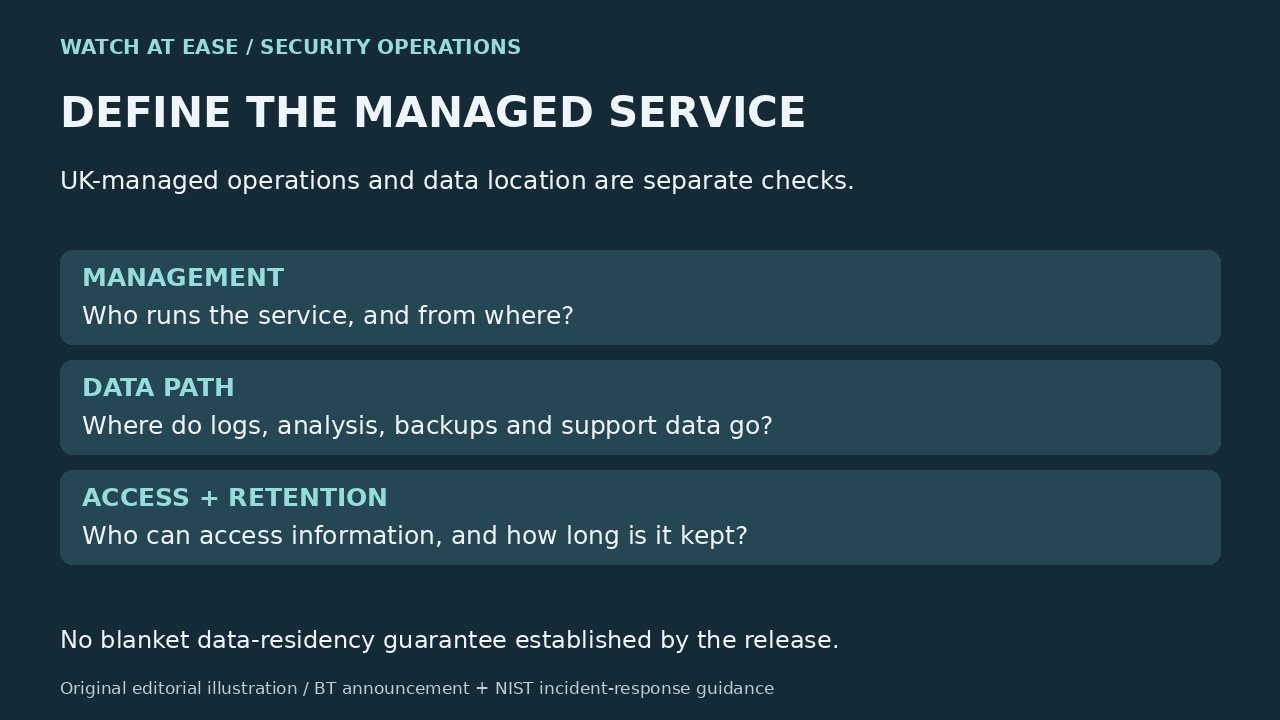
“UK-managed” describes the offer’s management. The release does not establish that every log, backup, analysis system or support interaction remains in the UK. Ask the supplier to describe the proposed data path, access arrangements and retention terms for your configuration, rather than turning the management label into a broader residency promise.
The announcement also does not publish contract pricing or measured response-time results. Request the actual coverage hours, escalation thresholds, service commitments and the method used to measure them. Include a practical incident exercise in the evaluation: an observed handoff and documented decision process provide more useful evidence than a broad promise about AI-era threats. These are suggested checks, not a report of testing the new service.